





Get your products ready for the Cyber Resilience Act
Annex I requirements, vulnerabilities, ENISA notifications and the CE marking file in one platform, product by product.


What the Cyber Resilience Act is and what it will ask of you
Regulation (EU) 2024/2847, the Cyber Resilience Act, requires cybersecurity from every product with digital elements sold in the EU: software, connected devices, components. Without it there is no CE marking, and without CE marking the product cannot be placed on the market.
It mainly binds manufacturers, but importers and distributors too. And anyone who sells a product under their own brand becomes the manufacturer for all purposes. Since 11 September 2026, actively exploited vulnerabilities and severe incidents must be reported, including for products already on the market. Everything else applies from 11 December 2027.
For the detail, read our guide on what the Cyber Resilience Act is and the practical part on how to comply with it.
- Regulation
- Regulation (EU) 2024/2847
- In force
- 10 December 2024
- Reporting
- Mandatory since 11 September 2026
- Full application
- 11 December 2027
- Fines
- Up to €15M or 2.5% of worldwide turnover
1
Role and products
You work out whether you are a manufacturer, importer or distributor and classify each product.
2
Risk and gaps
You assess each product’s risk and compare it against Annex I.
3
Vulnerabilities
SBOM, patches and on-time ENISA notifications for the whole support period.
4
CE marking
Technical documentation, conformity assessment and EU declaration.
How a product is classified
Default
Most products
The manufacturer assesses conformity on its own.
Class I
Important
Password managers, VPNs, routers… Harmonised standards or a notified body.
Class II
Important
Firewalls, hypervisors, intrusion detection… Always with a third party.
Critical
Critical
Smart cards or smart meter gateways. May require European certification.
Reporting deadlines:
24 h · early warning
72 h · notification
14 days · final vulnerability report
1 month · final incident report
The CRA in GlobalSuite®
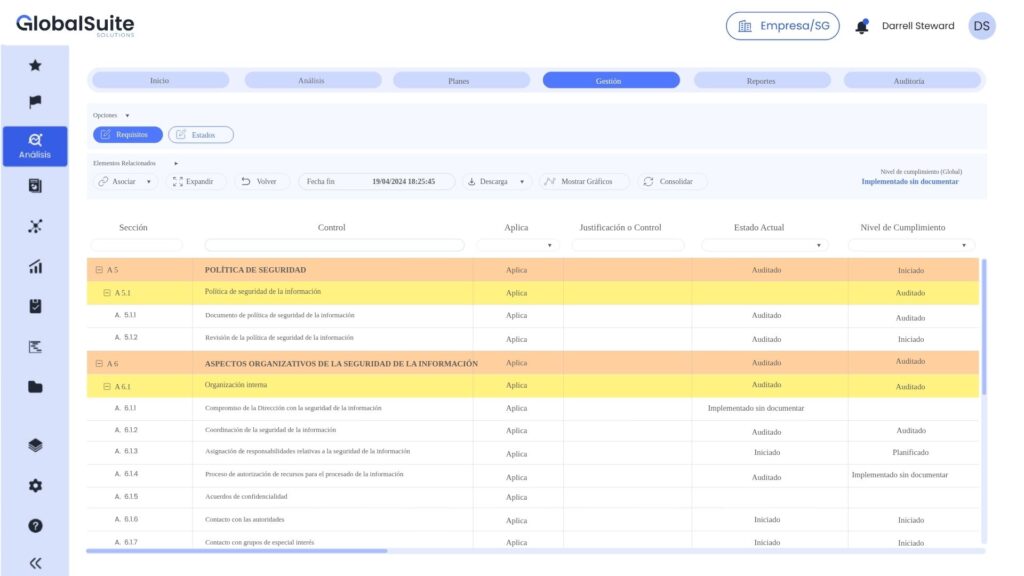
Each product with its classification, requirements, vulnerabilities and file. And each requirement linked to a control, an owner and a piece of evidence.
Compliance›Cyber Resilience Act›Products
Product inventory23 products · 7 important
CodeProductCategoryStatus
PRD-014
Home router R2
Manufacturer · support until 2032
Class IUnder reviewPRD-021
Smart home app
Manufacturer · support until 2031
DefaultCompliantPRD-009
Industrial gateway G7
Importer · support until 2034
Class IIGapPRD-030
Outdoor IP camera
Own brand · support until 2031
DefaultPartialCompliance›Cyber Resilience Act›Annex I · Home router R2
13
Requirements with evidence
5
Partial
3
No control
CodeRequirementOwnerStatus
I.2.b
Secure by default configuration
Part I · product requirements
ProductCoveredI.2.c
Automatic security updates
Part I · product requirements
FirmwarePartialII.1
Component SBOM
Part II · vulnerability handling
PSIRTCoveredII.5
Coordinated disclosure policy
Part II · vulnerability handling
CISONo controlCompliance›Cyber Resilience Act›Vulnerabilities and notifications
Vulnerabilities and notifications9 open · 1 actively exploited
VulnerabilityOwnerDeadlineStatus
Firmware TLS library · Router R2 · exploitedMIM. Ibáñez72 h · 31 h leftNotice pending
Early warning to ENISA · Router R2MIM. Ibáñez24 h · on timeSent
Default credential · IP cameraJRJ. RomeroPatch on 4 NovIn progress
Unsupported component in the SBOM · Gateway G7ALA. LeónReview on 20 NovIn progress
Compliance›Cyber Resilience Act›Mappings
MappingsAssessments reused from other standards
Requirement and related controlStatusStandard
I.2.d · Access controlReusedISO 27001
Art. 14 · Reporting severe incidentsReusedNIS2
I.2.f · Data and software integrityReusedIEC 62443
II.1 · Third-party componentsReviewThird parties
Notifications on time
When a vulnerability is flagged as exploited the clocks start, and every submission to ENISA and the CSIRT is logged.
Your suppliers included
SBOM components link to the third-party risk module: you know who supplies each part and whether it is still supported.
The file builds itself
Risks, controls and evidence are already in the platform. The technical documentation comes from there, not from a loose folder.
The CRA fits with what you already do
Cyber Resilience Act
Products, Annex I requirements, vulnerabilities, notifications and CE marking.
You are hereNIS2
The directive for organisations. The CRA does the same for the products they sell.
See solution →ISO 27001
If you already have an ISMS, a good share of the CRA controls is done.
See solution →Third-party risk
Your suppliers and the components they sell you, assessed and monitored.
See solution →
Cyber Resilience Act: frequently asked questions
Does it affect me if I don’t manufacture anything?
It may. Importers and distributors have their own obligations, and if you sell a product under your brand or substantially modify it, the Regulation treats you as the manufacturer.
What is already mandatory?
Since 11 September 2026, actively exploited vulnerabilities and severe incidents must be reported, including for products already on sale. The Annex I requirements, conformity assessment and CE marking apply from 11 December 2027.
Is software as a service covered?
Pure SaaS is out of scope, as NIS2 covers it. But if the cloud service is part of how a product works, such as the app that controls a device, it is covered as that product’s remote data processing solution.
How long do I have to provide support?
For as long as the product is expected to be used, with a minimum of five years unless its lifetime is shorter. During that period you must fix vulnerabilities and release security updates.
How does it relate to NIS2?
They complement each other. NIS2 asks the organisation for cybersecurity, and the CRA asks it of the products it places on the market. Many measures overlap, so in GlobalSuite® you work on them once and they count for both.
What is an SBOM?
The software bill of materials: the components and libraries inside the product. The CRA requires you to keep it so that, when a vulnerability appears, you know which products it affects.
The Cyber Resilience Act is Regulation (EU) 2024/2847 of the European Parliament and of the Council, published in the Official Journal of the European Union.
Your products ready
for the CRA.
We’ll show you Annex I, vulnerabilities and notifications in GlobalSuite®.