Keep your methodology
Your scales, your risk matrix, your appetite and your own catalogues. ISO 31000 doesn't impose a methodology, and neither does GlobalSuite®.
Platform
All-in-one GRC platform
AI built into every module
The common engine behind every module
GRC tailored to your industry
Connect GlobalSuite® to your tools
Standards and frameworks
ISO standards
Regulations
Document once, comply with all.
Resources
 Success storyEMT Madrid centralises its data protection management in GlobalSuite®Read the story

 G2 reviewsWhat the people who use GlobalSuite® every day say about itRead reviewsA customer? Leave a review
Popular searches
Know how much risk you accept and how much you carry right now. Identify, analyse, treat and monitor all your risks in one place, following the ISO 31000 process.
4.4 · 105 reviews on G2
2,000+ companies trust GlobalSuite®
What the standard asks for, what you've already done and what's still missing, all on one platform. Screens show sample data.
ISO 31000 isn't certified, it's measured. Each part of the framework and the process with its status and maturity.
ISO 31000 isn't certified, it's measured. Each part of the framework and the process with its status and maturity.
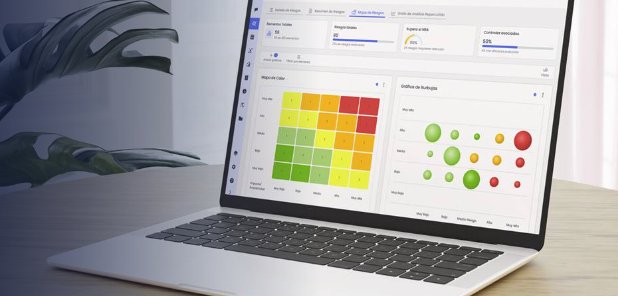
Likelihood and impact of each risk on two heat maps, inherent and residual, with the control that treats it.
Pick a risk in the area and the AI suggests treatment options to reduce it. Add them to the plan and the residual risk is recalculated.
Each risk indicator with its status, trend and latest value, plus its chart against the threshold.
Each area with its risk owner and the share of exposure it holds, ready for the committee.
Word and Excel templates for the risk committee and the board, filled in with up-to-date data.
You set up the workflow once and GlobalSuite® repeats it: it requests, reminds, collects and updates. Your team only steps in when there's a decision to make.
Your scales, your risk matrix, your appetite and your own catalogues. ISO 31000 doesn't impose a methodology, and neither does GlobalSuite®.
Risk map, profile against appetite and board report, up to date and ready to download.
Before each committee, the agent goes through the risks, finds those with no owner, control or KRI and drafts the plan. You just approve it.
The risk method is the same one COSO ERM, ISO 27001 and ISO 22301 call for. In GlobalSuite® every risk and every control counts for all of them.
Our own estimate of how much of each standard is covered: each requirement counts in full if it is covered the same way and half if only partly. Each standard adds its own requirements.
GlobalSuite® connects to your ecosystem via API. Data comes in on its own and nobody has to copy it by hand.
 Power BI
Monitoring
Vulnerabilities
Data lake
And the module is part of the GRC platform. Its process underpins all the others: security, continuity, third parties and compliance use the same risks, scales and controls, so you get a single view of the company's risk.
If you're asked for ISO 27001, DORA or COSO ERM tomorrow, the risk method is already in place.
Your team leads the way. GlobalSuite® automates your management system and, if you need it, our consultants support you at whichever step you choose.

Rail transport · 14,000+ employees
As we rolled out risk management and compliance processes, and given the size of the company and the range of its activities, we needed software that would make risk management more effective and efficient.
Diego Molero AlonsoDirector of Internal Audit, Compliance and Business Risk · Renfe
Simple and focused on what matters. I implemented it in a large company (more than 30k employees across the world) in 2 months with the support of GlobalSuite consultants.
It allows us to adapt risk matrices, evaluation methodologies, workflows, and reporting to fit each client's needs, which is very important as each organization has its own way of managing risk.
What has benefited us most is how easily the risk analysis calculation methodology can be configured, along with the fact that it supports more than two methodologies.
Shall we look at it with your risks and your methodology?
Request a demo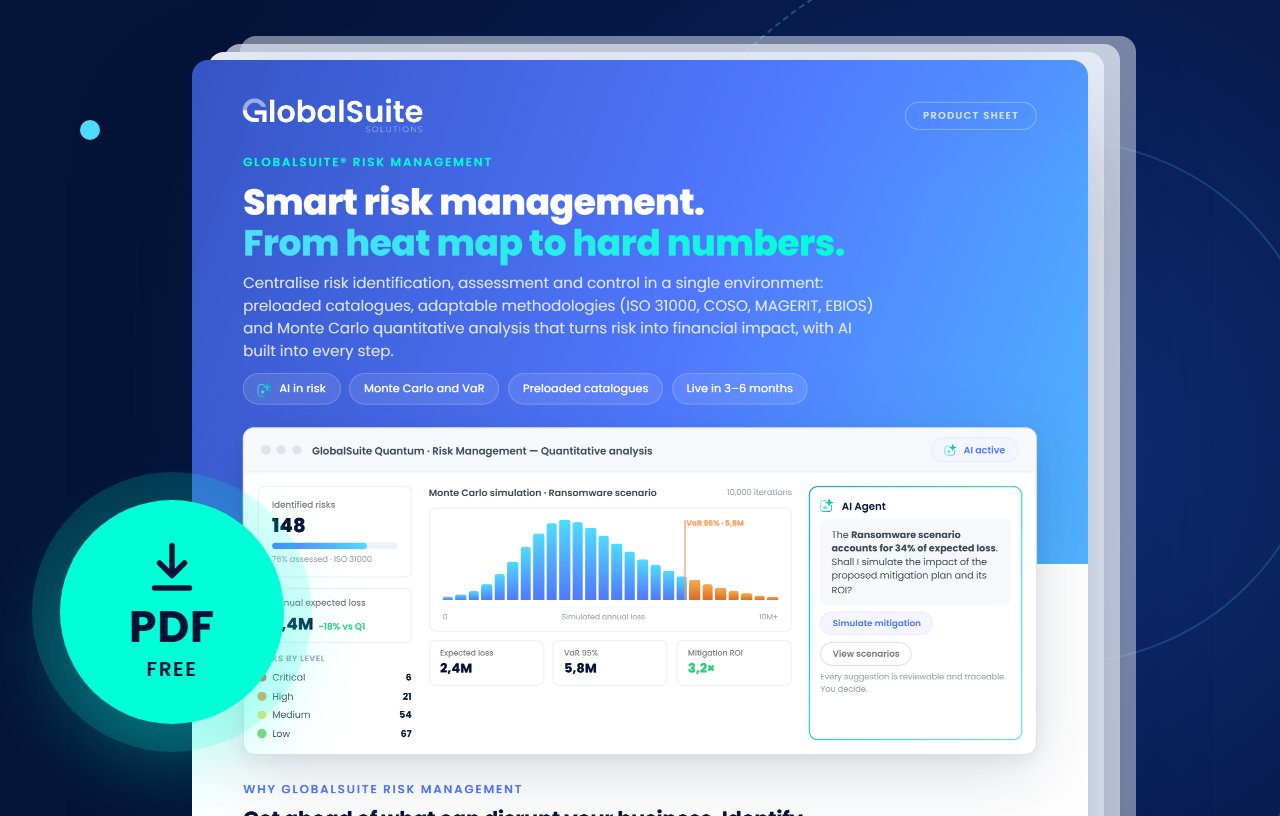 Product sheetGlobalSuite® RiskIdentification, analysis, treatment and KRIs for all your risks in one place, with ISO 31000 preloaded.Download PDF
A step-by-step method to assess risks and controls and present the results to management.
Download guideCan't find your question? Tell us about your case and we'll answer it with your situation in mind.
Tell us about your caseTell us what you need and we’ll show you how GlobalSuite® solves it.


