Keep your methodology
Your record, your clauses, your risk scales and your own controls. You start with what you already have.
Platform
All-in-one GRC platform
AI built into every module
The common engine behind every module
GRC tailored to your industry
Connect GlobalSuite® to your tools

Standards and frameworks
ISO standards
Regulations
Document once, comply with all.
Resources
 Success storyEMT Madrid centralises its data protection management in GlobalSuite®Read the story

 G2 reviewsWhat the people who use GlobalSuite® every day say about itRead reviewsA customer? Leave a review
Popular searches
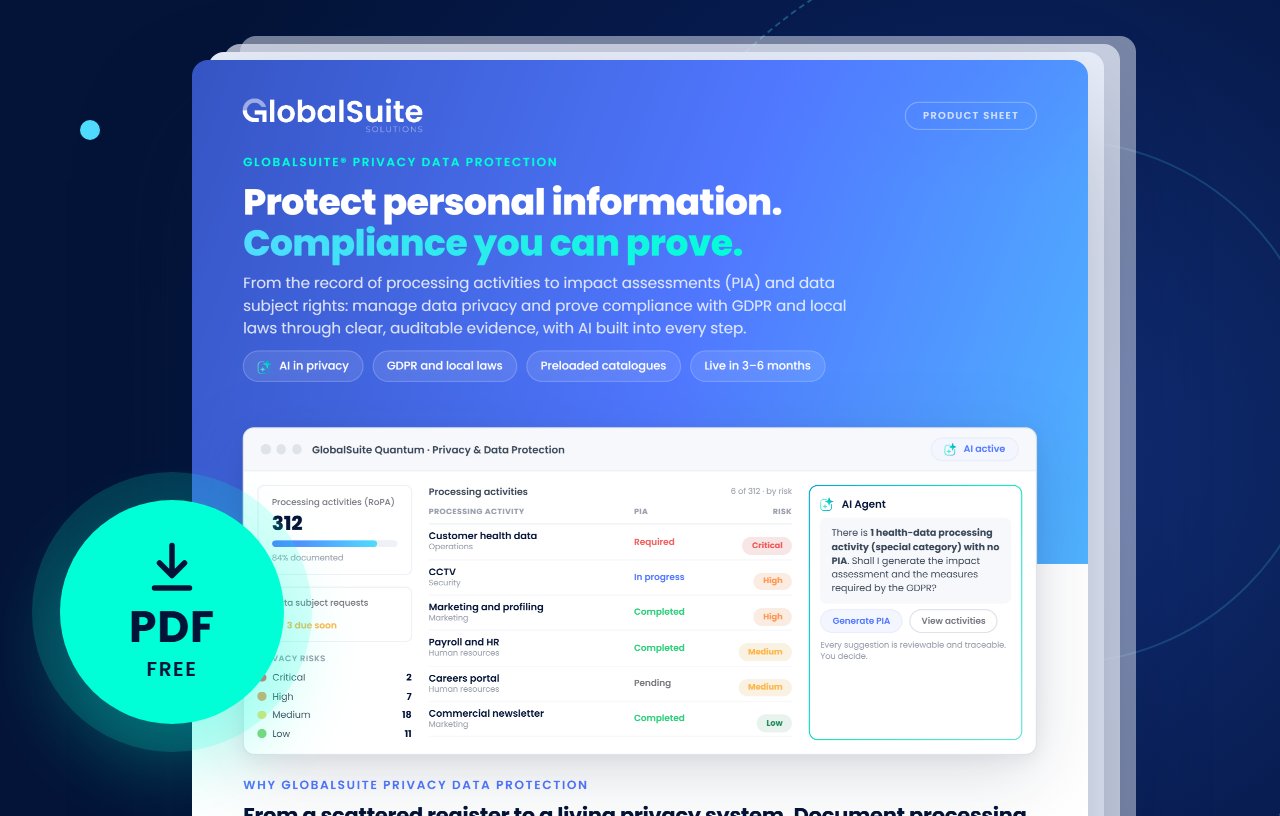
Everything GDPR asks for in one place: record of processing activities, legal bases, impact assessments, processors, breaches and the annual audit with its findings, ready to show the supervisory authority.
4,4 · 105 reviews on G2
2,000+ companies trust GlobalSuite®
What the Regulation asks for, what you've already done and what's still missing, all on one platform. Screens show sample data.
Every article of the Regulation with its applicability, status and level of compliance, ready to demonstrate.
Every article of the Regulation with its applicability, status and level of compliance, ready to demonstrate.
The annual audit, activity by activity: risks reviewed, controls tested and open findings.
The proof behind each legal basis in its folder: legitimate interest assessments and consents, with version and approval.
The AI reviews your consent indicators and suggests the ones that check whether the banner complies, not just how much is accepted.
How compliance rises from one assessment to the next, article by article.
Reports come from Word and Excel templates filled with platform data: the record, the DPO report or a breach notification.
You set up the workflow once and GlobalSuite® repeats it: it requests, reminds, collects and updates. Your team only steps in when there's a decision to make.
Your record, your clauses, your risk scales and your own controls. You start with what you already have.
Record of processing activities, impact assessments and audit report, up to date and ready to download.
Before each audit, the agent goes through the record, finds processing with no legal basis, no DPIA or past its deadline, and drafts the plan. You just sign it off.
The record, impact assessments and processor contracts are the foundation of ISO 27701 and ISO 27018. In GlobalSuite® you do them once and they count for all of them.
Our own estimate of how much of each standard is covered: each requirement counts in full if it is covered the same way and half if only partly. Each standard adds its own requirements.
GlobalSuite® connects to your ecosystem via API. Data comes in on its own and nobody has to copy it by hand.
 Power BI
Monitoring
Vulnerabilities
Data lake
And the module is part of the GRC platform. The processing activities, systems and processors you add for GDPR are the same ones security and third-party risk use, so nothing is maintained twice.
If you want ISO 27701 certification tomorrow, most of the work is already done.
Your team leads the way. GlobalSuite® automates your management system and, if you need it, our consultants support you at whichever step you choose.

Retail · Ecuador
Along with a positive experience of the tool, I'd highlight the timely, accurate help from support whenever we had a question or spotted a problem.
María Lorena Paredes CastilloHead of Legal · Grupo El Rosado
The platform is perfect for parameterizing. I personally use it for compliance with the LOPDP.
It reduces tool fragmentation and centralizes all evidence, documentation, controls, and assessments in one place.
It is very easy to use, and when we have had a problem, the support people are very helpful. It is easy to implement.
Shall we look at it with your risks and your methodology?
Request a demoCan't find your question? Tell us about your case and we'll answer it with your situation in mind.
Tell us about your caseTell us what you need and we’ll show you how GlobalSuite® solves it.