Keep your methodology
Your scales, your risk matrix and your own controls sit alongside the ISO 27701 controls. You start with what you already have.
Platform
All-in-one GRC platform
AI built into every module
The common engine behind every module
GRC tailored to your industry
Connect GlobalSuite® to your tools
Standards and frameworks
ISO standards
Regulations
Document once, comply with all.
Resources
 Success storyEMT Madrid centralises its data protection management in GlobalSuite®Read the story

 G2 reviewsWhat the people who use GlobalSuite® every day say about itRead reviewsA customer? Leave a review
Popular searches
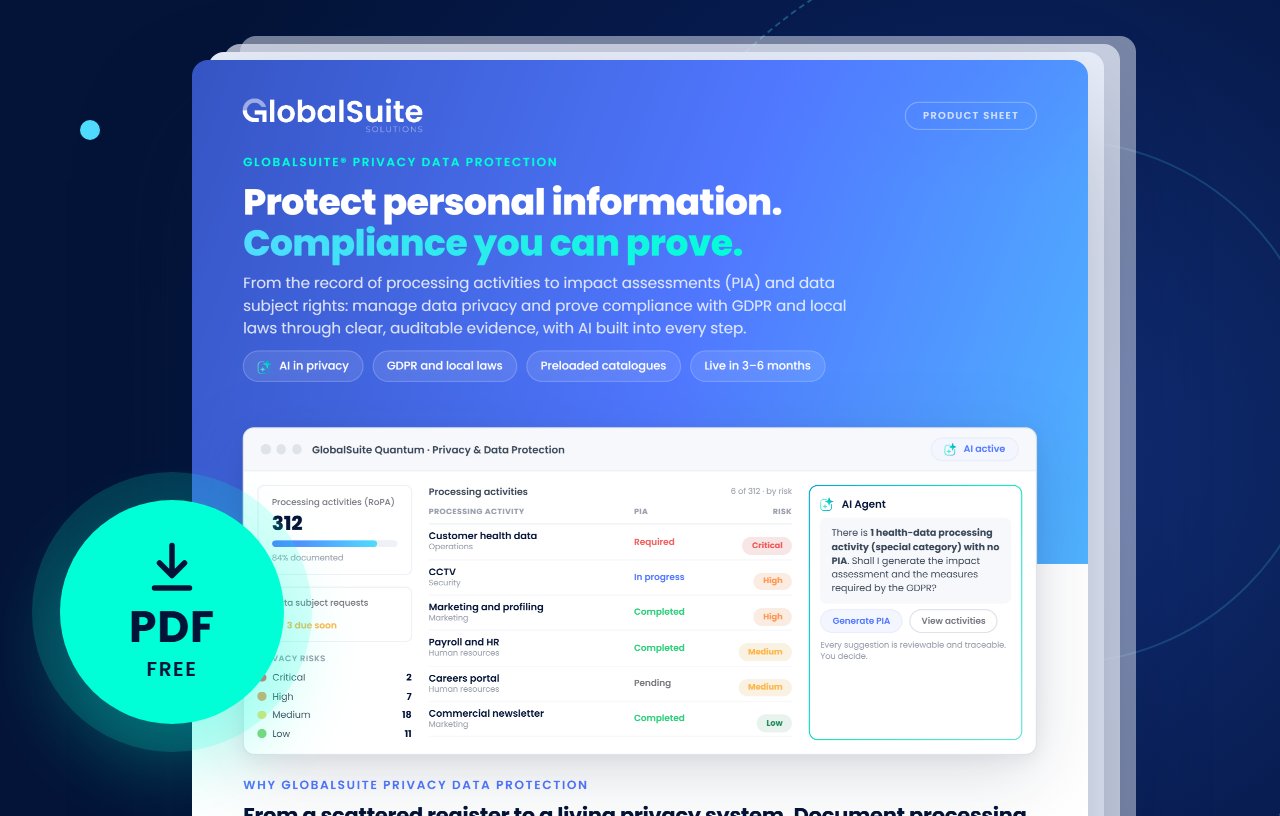
Know what personal data you process, where it is and who can see it. Record of processing activities, DPIAs, data subject rights and breaches in one place, aligned with the GDPR.
4.4 · 105 reviews on G2
2,000+ companies trust GlobalSuite®
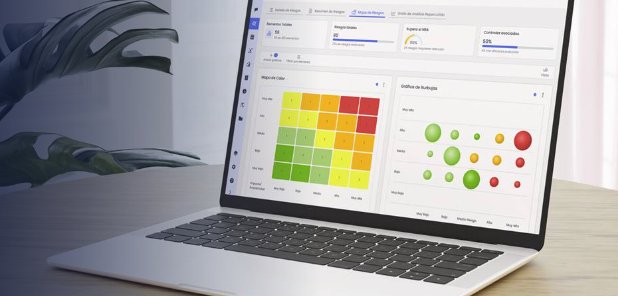
What the standard asks for, what you've already done and what's still missing, all on one platform. Screens show sample data.
Every Annex A control with its applicability, status and level of compliance, as controller and as processor.
Every Annex A control with its applicability, status and level of compliance, as controller and as processor.
The record of processing activities inside the inventory, each activity with its valuation.
Pick a processing risk and the AI suggests the ISO/IEC 27701 controls that reduce it. Add them to the plan and the residual risk is recalculated.
Data subject rights tracked with indicators: on-time responses, erasures applied and requests of each type.
Each personal data breach logged as an incident, with its priority, status, affected service and an alert when it must be notified.
Each processor with its country and valuation, and the questionnaire it completes before processing data for you.
The Power BI dashboard for the DPO and management: compliance by standard, by section and by status of each control.
You set up the workflow once and GlobalSuite® repeats it: it requests, reminds, collects and updates. Your team only steps in when there's a decision to make.
Your scales, your risk matrix and your own controls sit alongside the ISO 27701 controls. You start with what you already have.
Record of processing activities, DPIAs and DPO report, up to date and ready to download.
Before each audit, the agent goes through the record, finds the processing activities with no lawful basis or no assessment and drafts the plan. You just sign it off.
The record, the DPIAs and the processor contracts are the foundation of the GDPR and the other privacy standards. In GlobalSuite® you do them once and they count for all of them.
Our own estimate of how much of each standard is covered: each requirement counts in full if it is covered the same way and half if only partly. Each standard adds its own requirements.
GlobalSuite® connects to your ecosystem via API. Data comes in on its own and nobody has to copy it by hand.
 Power BI Monitoring Vulnerabilities Data lake
And the module is part of the GRC platform. The processing activities, systems and processors you add for ISO 27701 are the same ones that security and third-party risk use, so nothing is maintained twice.
If you already have ISO 27001, privacy builds on top of it without starting from scratch.
Your team leads the way. GlobalSuite® automates your management system and, if you need it, our consultants support you at whichever step you choose.

Retail · Ecuador
Along with a positive experience of the tool, I'd highlight the timely, accurate help from support whenever we had a question or spotted a problem.
María Lorena Paredes CastilloHead of Legal · Grupo El Rosado
The platform is perfect for parameterizing. I personally use it for compliance with the LOPDP.
It reduces tool fragmentation and centralizes all evidence, documentation, controls, and assessments in one place.
It is very easy to use, and when we have had a problem, the support people are very helpful. It is easy to implement.
Shall we look at it with your risks and your methodology?
Request a demoCan't find your question? Tell us about your case and we'll answer it with your situation in mind.
Tell us about your caseTell us what you need and we’ll show you how GlobalSuite® solves it.