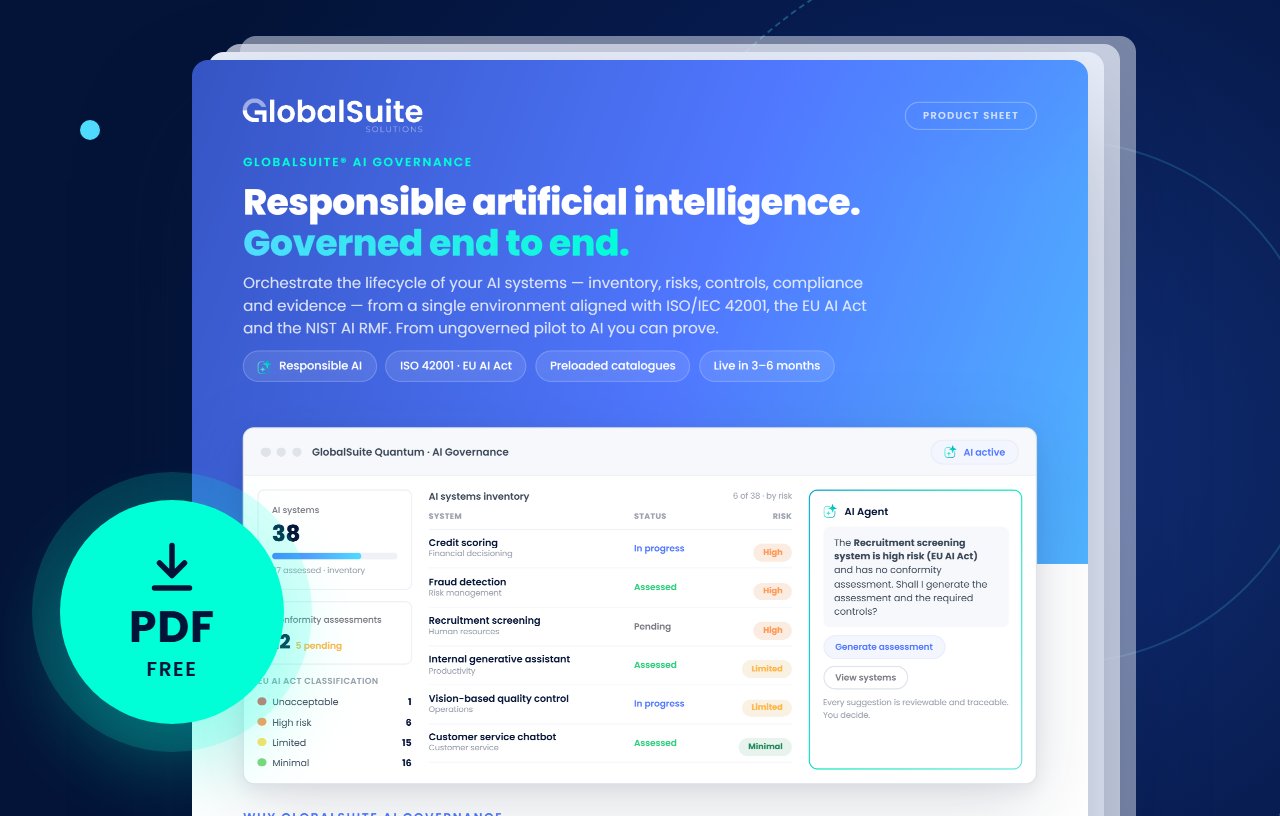
Keep your methodology
Your scales, your risk matrix and your own controls sit alongside the ISO 42001 Annex A controls. You start with what you already have.
Platform
All-in-one GRC platform
AI built into every module
The common engine behind every module
GRC tailored to your industry
Connect GlobalSuite® to your tools

Standards and frameworks
ISO standards
Regulations
Document once, comply with all.
Resources
 Success storyEMT Madrid centralises its data protection management in GlobalSuite®Read the story

 G2 reviewsWhat the people who use GlobalSuite® every day say about itRead reviewsA customer? Leave a review
Popular searches
Knowing which AI your company uses is the first step. Inventory, impact assessment, risks and Annex A controls in one place, aligned with the EU AI Act.
4.4 · 105 reviews on G2
2,000+ companies trust GlobalSuite®
What the standard asks for, what you've already done and what's still missing, all on one platform. Screens show sample data.
Every Annex A control with its applicability, its status and its level of compliance.
Every Annex A control with its applicability, its status and its level of compliance.
Every AI system in the inventory, with its origin and its confidentiality, integrity, availability and importance ratings.
The AI compares the impact assessment with those of similar systems and adds the missing dimensions. The owner only has to answer them.
Accuracy, drift and oversight of each model as indicators, with their target, their trend and a month-by-month chart.
Every system moves through its stages with its own approval workflow. Nothing is deployed until the right people approve it.
The AI Act articles for high-risk systems at each review: what ISO 42001 already covers and what is still open.
The compliance dashboard across all your standards: by catalogue, by Annex A objective and by control status.
You set up the workflow once and GlobalSuite® repeats it: it requests, reminds, collects and updates. Your team only steps in when there's a decision to make.
Your scales, your risk matrix and your own controls sit alongside the ISO 42001 Annex A controls. You start with what you already have.
Statement of Applicability, AI system inventory and committee dashboard, up to date and ready to download.
Before each audit, the agent goes through the inventory, finds the systems with no impact assessment and drafts the plan. You just sign it off.
The inventory, the impact assessment and the life cycle controls are the foundation of the AI Act and the NIST AI RMF. In GlobalSuite® you do them once and they count for all of them.
Our own estimate of how much of each standard is covered: each requirement counts in full if it is covered the same way and half if only partly. Each standard adds its own requirements.
GlobalSuite® connects to your ecosystem via API. Data comes in on its own and nobody has to copy it by hand.
 Power BI Monitoring Vulnerabilities Data lake
And the module is part of the GRC platform. The systems, data and suppliers you register for ISO 42001 are the same ones used by privacy, security and third-party risk, so nothing is maintained twice.
When the AI Act applies to you, you start with the inventory and the assessments already done.
Your team leads the way. GlobalSuite® automates your management system and, if you need it, our consultants support you at whichever step you choose.

Rail transport · 14,000+ employees
As we rolled out risk management and compliance processes, and given the size of the company and the range of its activities, we needed software that would make risk management more effective and efficient.
Diego Molero AlonsoDirector of Internal Audit, Compliance and Business Risk · Renfe
It reduces tool fragmentation and centralizes all evidence, documentation, controls, and assessments in one place.
Simple and focused on what matters. I implemented it in a large company (more than 30k employees across the world) in 2 months with the support of GlobalSuite consultants.
It is very easy to use, and when we have had a problem, the support people are very helpful. It is easy to implement.
Shall we look at it with your risks and your methodology?
Request a demoCan't find your question? Tell us about your case and we'll answer it with your situation in mind.
Tell us about your caseTell us what you need and we’ll show you how GlobalSuite® solves it.