





COBIT, from framework to evidence
Assess the capability of your IT governance and management objectives, prioritise improvements and show the board the data.


What COBIT is and what you will be asked for
COBIT is the ISACA framework for governing and managing an organisation’s information and technology. It separates what the board decides (governance) from what IT leadership carries out (management), and organises it all into 40 objectives across five domains.
Internal and external auditors, boards and supervisors ask for it when they want to know whether IT is under control and aligned with the business. The organisation itself is not certified. What gets measured is the capability of each objective, from 0 to 5, against a target level you set.
- Published by
- ISACA
- Version
- COBIT 2019
- Structure
- 40 governance and management objectives in 5 domains
- Measurement
- Capability levels from 0 to 5 per process
- Certification
- For individuals, not organisations
1
Design factors
Strategy, risk, size and context decide which objectives matter most.
2
Priority objectives
You pick the objectives to work on and their target capability level.
3
Assessment
You measure each process’s current capability through its activities and evidence.
4
Improvement plan
Gaps become actions, and progress is reported to the board.
The five domains
EDM
Evaluate, Direct and Monitor
Governance: what the board decides and oversees.
APO
Align, Plan and Organise
Strategy, architecture, risk and suppliers.
BAI
Build, Acquire and Implement
Projects, changes, assets and configuration.
DSS
Deliver, Service and Support
Operations, incidents, continuity and security.
MEA
Monitor, Evaluate and Assess
Performance, internal control and compliance.
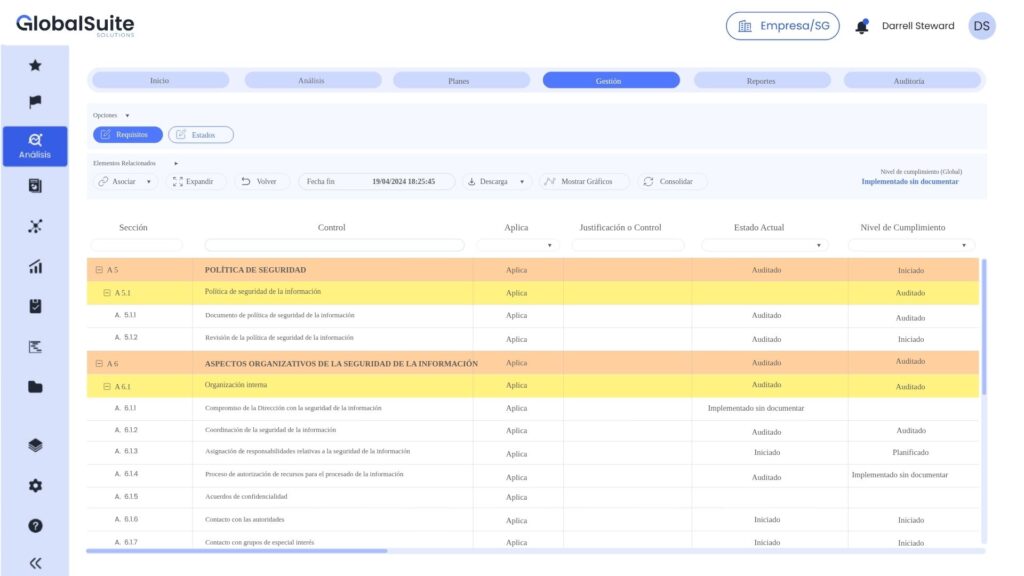
Govern your IT with COBIT in GlobalSuite®
Objectives, capability, actions and reports in one place, with every process linked to its owner and its evidence.
Compliance›COBIT 2019›Objectives
Priority objectives12 of 40 objectives in scope
CodeObjectiveOwnerTarget
EDM03
Ensured Risk Optimisation
Governance
BoardLevel 3APO12
Managed Risk
Align, Plan and Organise
CROLevel 3BAI06
Managed IT Changes
Build, Acquire and Implement
IT Dir.Level 3DSS05
Managed Security Services
Deliver, Service and Support
CISOLevel 4Compliance›COBIT 2019›Capability assessment
5
On target
6
Below target
1
Not assessed
CodeObjectiveCapability / targetLevel
EDM03Ensured Risk Optimisation3
APO12Managed Risk2
APO13Managed Security2
BAI06Managed IT Changes3
DSS05Managed Security Services2
Compliance›COBIT 2019›Improvement plan
Improvement plan18 actions · 9 closed
ActionOwnerDateStatus
IT risk appetite approved by the boardCRC. Ruiz20 NovIn progress
Change advisory board with recorded minutesJOJ. Ortega12 NovClosed
Regular review of privileged accessPMP. Molina30 NovOpen
Security KPIs on the dashboardALA. León5 DecIn progress
Reports›COBIT 2019›Board
Board reportingNext audit committee: December
ReportStatusGenerated
State of IT governance · Q3Sent2 wk
Capability gaps by domainUp to datetoday
Improvement plan trackingDraft3 d
Open internal audit findingsUp to date1 wk
One control, several standards
Map your COBIT objectives to ISO 27001, ISO 20000 or NIS2 controls. One piece of evidence covers them all.
IT risk where it belongs
APO12 runs on the risk module: scenarios, assessment and treatment with your own methodology.
Internal audit built in
Plan reviews of each objective, log findings and track them to closure in the same place.
COBIT fits with what you already do
COBIT
IT governance and management objectives, capability, improvement plan and reporting.
You are hereISO 27001
The information security COBIT asks you to govern, with its own management system.
See solution →ISO 20000
Certifiable IT service management that covers much of the BAI and DSS domains.
See solution →Risk management
The GlobalSuite® risk module, the foundation for APO12 and EDM03.
See solution →
COBIT frequently asked questions
Can a company get COBIT certified?
No. COBIT is a reference framework, not a certifiable standard for organisations. ISACA does issue certifications for individuals. What an organisation can show is the capability level of its processes, usually to internal or external auditors.
What is the difference between governance and management?
Governance sits with the board: it evaluates, directs and monitors (EDM domain). Management sits with the executive team: it plans, builds, runs and monitors IT in line with those decisions (APO, BAI, DSS and MEA domains).
What is a capability level?
It measures how well a process works, from 0 (incomplete) to 5 (continuously improving). In COBIT 2019 each process activity is tied to a level, and the process reaches that level once it carries those activities out.
Do I have to work on all 40 objectives?
No. Design factors (strategy, risk profile, size, context) exist precisely to prioritise the objectives that matter most to your organisation and set a realistic target level for each one.
Does COBIT replace ISO 27001 or ITIL?
No, they complement each other. COBIT says what needs to be governed and managed in IT. ISO 27001 and ITIL give the detail on how to do it for security and services. Many organisations use COBIT as the umbrella and the other standards for day-to-day operations.
Where do I start?
With the design factors and a first assessment of your priority objectives. There is more background in our guide to implementing an IT risk framework.
COBIT® is a registered trademark of ISACA.
IT governance
you can measure.
We’ll walk you through your COBIT assessment in GlobalSuite®.