





COSO ERM: risk, connected to your strategy
Risk appetite, key risk indicators, responses and board reporting on one platform, built around the five components of COSO ERM.


What COSO ERM is and what you’ll be asked for
COSO ERM is the enterprise risk management framework from the Committee of Sponsoring Organizations of the Treadway Commission. The 2017 edition, Integrating with Strategy and Performance, starts from a simple idea: you manage risk at the same time as you set strategy and measure performance.
It isn’t a law and you can’t be certified against it, but boards, audit committees and supervisors use it as the benchmark to check that the business knows how much risk it is willing to take on and how it keeps an eye on it. It is built on five components and twenty principles.
- Published by
- COSO, Committee of Sponsoring Organizations of the Treadway Commission
- Edition
- 2017, Integrating with Strategy and Performance
- Structure
- 5 components and 20 principles
- Certifiable
- No, it is a reference framework
- Works with
- COSO Internal Control 2013 and ISO 31000
1
Risk appetite
The board sets how much risk it is prepared to accept to deliver the strategy.
2
Identification
Each area identifies and assesses the risks that affect its objectives.
3
Response
Risks are prioritised and each one is accepted, reduced, shared or avoided.
4
Monitoring
Key risk indicators and regular reporting to the board and audit committee.
The five components of COSO ERM
1
Governance & Culture
Board oversight, accountability structures and the organisation’s risk culture.
2
Strategy & Objective-Setting
Risk appetite is defined alongside the strategy and business objectives.
3
Performance
Identify, assess, prioritise and respond to the risks that affect your objectives.
4
Review & Revision
Check that risk management still works as the business changes.
5
Information, Communication & Reporting
Risk information reaches the people who decide, in time to act on it.
Put COSO ERM to work in GlobalSuite®
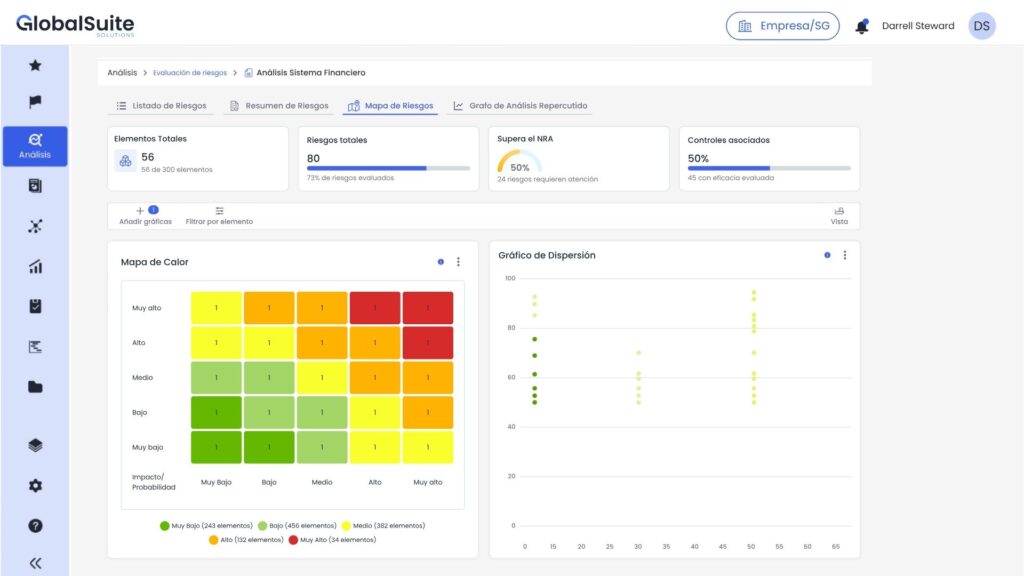
From risk appetite to board reporting in one place, with every risk linked to an objective and an owner.
Risks›COSO ERM›Risk appetite
Key risk indicators12 KRIs · 2 outside tolerance
KRIIndicatorValue / thresholdValue
K-01Customers making up 50% of sales66
K-02Debt overdue by more than 90 days48
K-03Critical suppliers with no alternative78
K-04Key staff turnover35
Risks›COSO ERM›Risks by objective
Strategic plan 2026-20284 objectives · 27 risks
CodeRiskObjectiveLevel
R-03
Delay in entering new markets
Licences and local partners
GrowthHighR-07
Reliance on a single supplier
Component with no alternative
OperationsHighR-11
Cyberattack on the plant
Industrial control systems
OperationsMediumR-15
EU regulatory change
Sustainability reporting
ReputationLowRisks›COSO ERM›Responses
Response plans9 actions · 4 closed
ActionOwnerDueStatus
Approve a second supplierACA. Castro31 DecIn progress
Export credit insuranceJMJ. Martín15 NovClosed
Segment the plant networkINI. Navarro28 FebOpen
Succession plan for key rolesBSB. Soler31 MarIn progress
Risks›COSO ERM›Board reporting
2
KRIs outside tolerance
5
High risks
4
Actions closed
ComponentStatusReviewed
Governance & CultureUp to dateSep
Strategy & Objective-SettingUp to dateJul
Review & RevisionPendingMar
Risk and strategy in one place
Your strategic objectives and the risks that threaten them, connected. When an objective changes, you see which risks change with it.
Your methodology, not ours
Configurable impact and likelihood scales, appetite criteria and response types. You can combine COSO ERM with ISO 31000.
From the front line to the board
Each owner updates their own risks and indicators, and the board gets the full picture without anyone merging spreadsheets by hand.
COSO ERM fits with what you already do
COSO ERM
Risk appetite, key risk indicators, responses and board reporting.
You are hereISO 31000
The international risk management standard, compatible with COSO ERM.
View solution →Risk management
The GlobalSuite® module your COSO ERM model is built on.
View solution →Internal audit
Test how well your risk management works as part of your audit plan.
View solution →
COSO ERM: frequently asked questions
How is COSO ERM different from COSO Internal Control?
COSO Internal Control (2013) focuses on the controls that make information and operations reliable. COSO ERM (2017) is broader: it covers how the organisation identifies and manages the risks that affect its strategy. They complement each other and many organisations use both.
Can you get certified in COSO ERM?
No. It is a reference framework, not a certifiable standard. What organisations do is assess the maturity of their risk management against its components and principles, usually through internal audit.
How does it compare with ISO 31000?
Both aim for the same thing. ISO 31000 is a shorter, more general international standard; COSO ERM goes into more detail and is widely used in corporate governance and audit settings. You can combine them in the same methodology without any trouble.
What is risk appetite?
The amount of risk an organisation is willing to accept to achieve its objectives. The board sets it, and it is turned into thresholds and key risk indicators that show you early on if you are drifting outside it.
Where do you start?
With your strategic objectives and risk appetite. Once those are clear, each area identifies its risks, they are rated on the same scale and you choose the indicators you will track. There is more background in our article What is the COSO model?
Risk and strategy,
in one place.
We’ll show you your risk appetite and key indicators in GlobalSuite®.