
TPRMThird-Party Risk Management
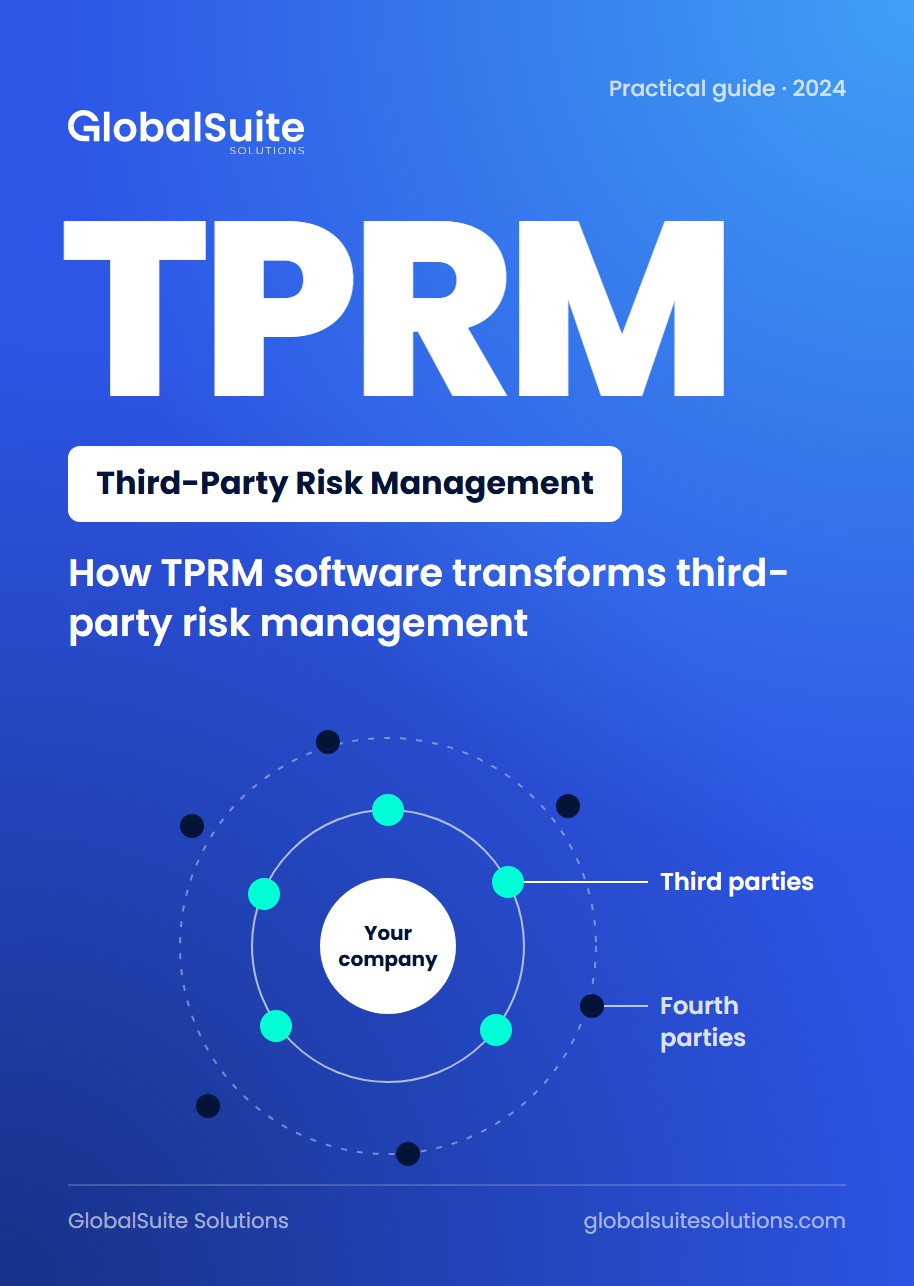
How a TPRM Software Can Transform Third-Party Risk Management
What third-party risk is, what a TPRM tool should do and three real use cases.
Download the guidePlatform
All-in-one GRC platform
AI built into every module
The common engine behind every module
GRC tailored to your industry
Connect GlobalSuite® to your tools

Standards and frameworks
ISO standards
Regulations
Document once, comply with all.
Resources
 Success storyEMT Madrid centralises its data protection management in GlobalSuite®Read the story

 G2 reviewsWhat the people who use GlobalSuite® every day say about itRead reviewsA customer? Leave a review
Popular searches
Informative, up-to-date content on management, compliance, and cybersecurity. In this section, you’ll find analyses, practical advice, and guides designed to help you improve your processes and make informed decisions.
What third-party risk is, what a TPRM tool should do and three real use cases.
Download the guide
A practical guide to risk quantification: what it is, why to quantify by scenario rather than risk by risk, how Monte C…
Read more
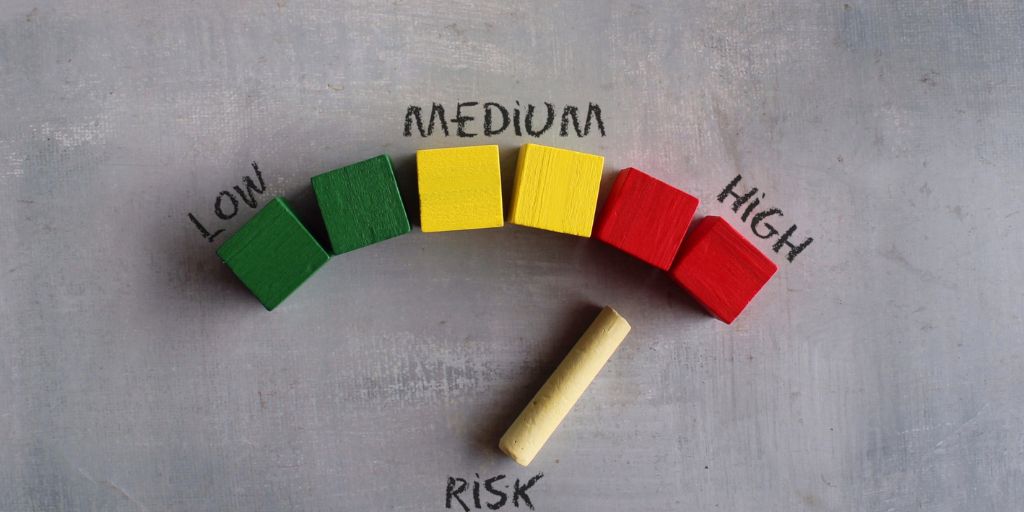
How to build a risk map following ISO 31000, how to read a heat map with an example of seven risks, and what risk manag…
Read more
What key risk indicators (KRIs) are, how to define them around likelihood, impact, risk value or control effectiveness,…
Read more
A comparison of three well-known information security risk assessment methods, MEHARI, EBIOS and OCTAVE: who created th…
Read more
What the COSO model is, how it has evolved, the components and principles of COSO 2013 internal control and COSO ERM 20…
Read more