


There is no doubt that identifying and assessing risks (and mapping them) is now one of the unavoidable pillars of running any company. In an increasingly global context, exposed to constant changes that can affect companies in one way or another, being able to anticipate situations that could have a negative impact gives organisations a competitive edge that helps them achieve their objectives.
To do this, organisations need procedures that allow them to identify the potential threats that could harm their processes, services or activities, and to analyse the controls already in place that help to reduce the likelihood and impact if those threats materialise. They also need to be able to take additional measures to reduce the risks that exceed the level of risk the company considers acceptable.
Risk management and risk mapping with ISO 31000
For this purpose, ISO 31000 gives a detailed description of a systematic risk management process and sets out a series of principles that, when followed, ensure risk is managed effectively. Although the standard is not certifiable, it brings companies considerable benefits. As the standard itself puts it, “the purpose of risk management is the creation and protection of value. It improves performance, encourages innovation and supports the achievement of objectives”. So what principles do you need to follow to manage risk effectively and efficiently?
- Integrated: risk management is an integral part of all the organisation’s activities.
- Structured and comprehensive, so that it produces consistent and comparable results.
- Customised and proportionate to the organisation’s internal and external context.
- Inclusive, with appropriate involvement of all the interested parties concerned.
- Dynamic, because risks can emerge, change or disappear, and the organisation must be able to anticipate, detect, acknowledge and respond to those changes appropriately.
- Based on the best available information, both historical and current, as well as on expectations.
- Human and cultural factors, which have a significant influence on every level and stage of risk management.
- Continual improvement.
How to build a risk map
Turning to the process of building the risk map itself, it consists of the following stages:
- Risk identification: this stage involves finding, recognising and describing the risks that could get in the way of the organisation’s objectives. To identify risks properly, you need to meet the people who know each of the organisation’s areas and processes well and are therefore able to carry out that identification.
- Risk analysis: This is the stage where you consider in detail “ uncertainties, risk sources, consequences, likelihood, events, scenarios, controls and their effectiveness”. In essence, you establish the likelihood of the risk occurring and the impact of its consequences by rating and assessing them. The aim is to determine the organisation’s level of risk as accurately as possible.
- Risk evaluation: Once the risk analysis is done, you need to look at the results to make decisions about risk treatment. This stage of analysis and decision is called risk evaluation. In general, there are four ways of treating the risks identified:
- Reduce the level of risk by putting in place the measures considered appropriate.
- Transfer the risk to a third party, either by taking out insurance or by outsourcing the activity so that the contracted organisation manages the risk.
- Accept the risk, so that the organisation takes no action and bears the consequences if the threat materialises.
- Stop the activity associated with the risk, removing the likelihood of it occurring.
- Risk treatment: treating risk means selecting and implementing options to address it. For the risks the organisation does not accept, a treatment plan has to be drawn up that sets out the measures to implement, deadlines, owners and a description of the activities to carry out. The plan’s progress should be followed up regularly so you always know where each measure stands.
How to read a risk map
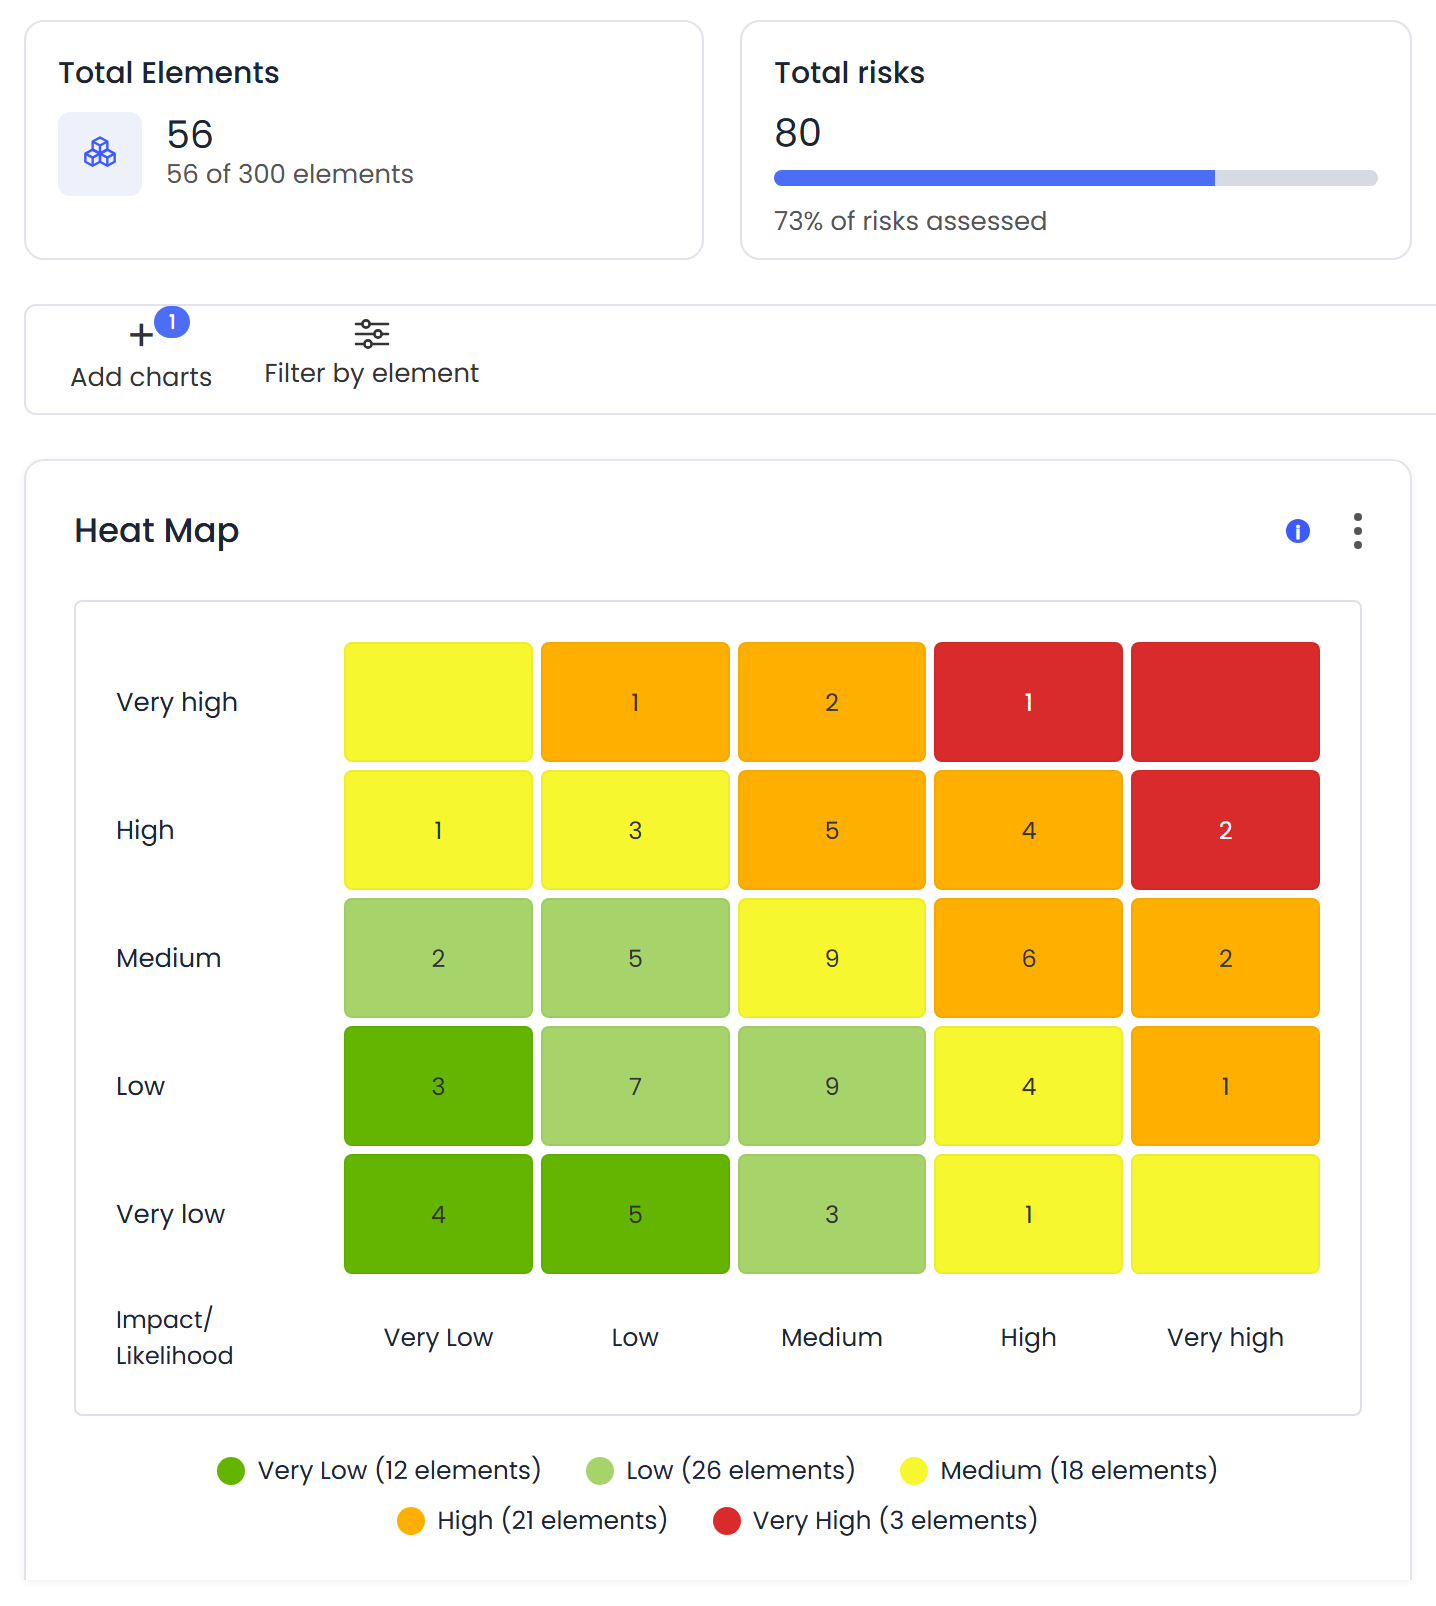
The result of these stages is plotted on a likelihood by impact matrix: the heat map. Each risk falls into the cell that matches its rating, and the colour of the cell shows its level. At a glance you can see what needs treating first.
What gives the map its meaning is the line between what is acceptable and what is not, in other words the risk appetite translated into the map's scale. If, in the example, the organisation sets its acceptable level at 9, ransomware (R1), the data breach (R2), procurement fraud (R6) and supplier delays (R7) need a treatment plan. The rest are accepted and monitored.
It is worth drawing the map twice: once with the risk before controls and once with what remains after them. The comparison shows how much the controls are contributing, and it is what gets presented to the committee. We explain it with an example in inherent risk and residual risk.
Benefits of managing risk maps with software
Having gone through the whole process set out in ISO 31000, it is hard not to conclude that implementing it efficiently and effectively calls for a software tool that automates the process. It is a collaborative effort between several areas of the organisation, each with different responsibilities, which together achieve the final goal.
The benefits of implementing a risk management software platform are many. Here are three of the most important:
- Centralised identification of all the risks to be analysed. The information gathered in working sessions with the different area and process owners can be organised as a risk catalogue to be used later in the risk analysis. These catalogues build a knowledge base of the organisation’s typical risks, which can be reused for similar new areas or processes in the future.
- An automated risk analysis process. A software tool with sufficient integrity safeguards ensures that a risk analysis carried out by any owner always produces comparable results, because the calculation cannot be altered. And if the process is automated by sending out assessment questionnaires, it takes less time to gather all the information.
- Consolidation and traceability of all risks. Having all the information in one place means the organisation’s complete picture is consolidated and the final results are traceable. Consolidated reports are also quick and simple to produce, and you avoid the manual errors that come with handling information scattered across different sources.
In the GlobalSuite® Risk Management module the heat map comes straight out of the analysis: each cell shows how many risks it holds, and the ones above your acceptable level show up in red without anyone having to look for them.
At GlobalSuite Solutions we also help you implement your risk management system through the software, so that it fits into your organisation and brings the following advantages:
- You will increase the likelihood of achieving your business objectives;
- You will improve the identification of opportunities and threats;
- You will increase stakeholder confidence;
- You will improve your controls;
- You will allocate and use resources for risk treatment effectively, and
- You will improve loss prevention and incident management.