





Measure your cybersecurity with NIST CSF 2.0
Current profile, target profile and action plan on one platform, with the framework's six functions linked to the controls you actually run.


What NIST CSF is and what you'll be asked for
The Cybersecurity Framework from NIST, the US standards institute, is a framework for managing cybersecurity risk. Version 2.0, published in February 2024, now targets organisations of any size and sector and adds a sixth function, Govern.
It's voluntary and there's no certification, but it has become the common language for talking about cybersecurity with parent companies, customers and insurers, especially if you work with US businesses. What they'll ask you for is a profile: where you are, where you want to be and how you'll close the gap.
- Publisher
- NIST, US Department of Commerce
- Version
- CSF 2.0, February 2024
- Structure
- 6 functions, 22 categories and 106 subcategories
- Status
- Voluntary, no certification
- Output
- Current profile, target profile and action plan
1
Scope
You decide which part of the organisation is in and what the business needs.
2
Current profile
You assess each subcategory against today's controls and evidence.
3
Target profile
You set where you want to get to, based on your risk and obligations.
4
Action plan
The gap between the two profiles becomes a prioritised plan.
The six functions
GV
Govern
Strategy, roles, policies and oversight of cybersecurity risk, including the supply chain.
ID
Identify
Assets, risks and opportunities to improve.
PR
Protect
Access, awareness and training, data and platform security.
DE
Detect
Continuous monitoring and event analysis.
RS
Respond
Incident management, analysis, communication and containment.
RC
Recover
Getting back to normal and communicating the recovery.
Implementation Tiers:
1 · Partial
2 · Risk Informed
3 · Repeatable
4 · Adaptive
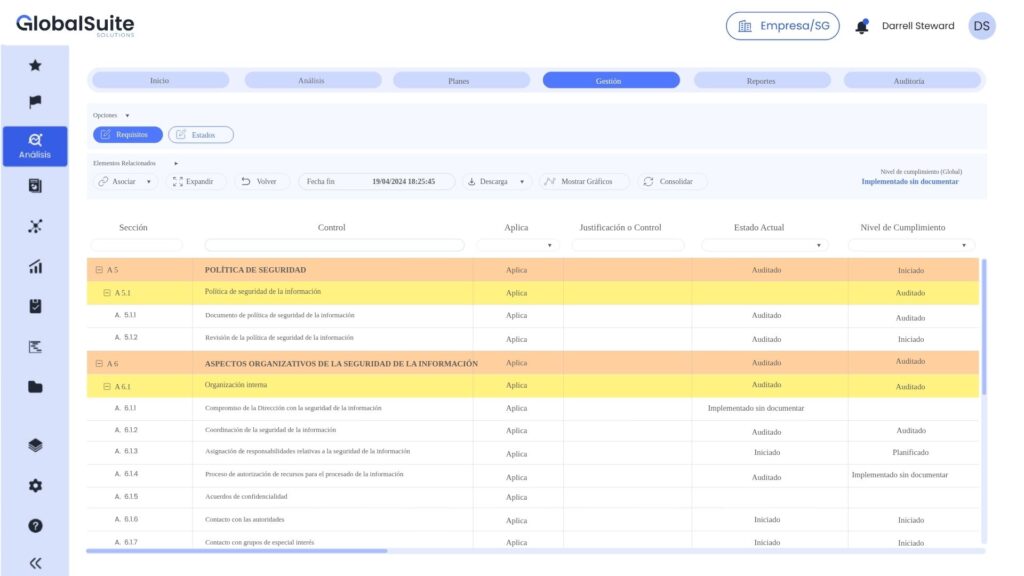
Your NIST CSF profile in GlobalSuite®
From scope to action plan in one place, with every subcategory linked to its controls, its owner and its evidence.
Compliance›NIST CSF 2.0›Current profile
Current profile106 subcategories · 81 assessed
CodeSubcategoryOwnerStatus
GV.RM-01
Risk management objectives agreed
Govern · risk strategy
CROPartialID.AM-01
Hardware inventory
Identify · asset management
ITImplementedPR.AA-01
Identities and credentials managed
Protect · access
CISOImplementedDE.CM-01
Network monitoring
Detect · continuous monitoring
SOCPendingCompliance›NIST CSF 2.0›Current vs target
2
Functions on target
4
Below target
25
Subcategories not assessed
FunctionNameCurrent / targetTier
GVGovern2
IDIdentify3
PRProtect3
DEDetect2
RSRespond2
Compliance›NIST CSF 2.0›Action plan
Action plan16 actions · 5 closed
ActionOwnerDueStatus
Cybersecurity risk appetite approvedFCF. Castro15 DecIn progress
Network monitoring across all sitesEPE. Prieto30 NovOpen
Cybersecurity requirements in supplier contractsIMI. Méndez10 DecIn progress
Incident response exerciseSGS. Gil8 NovClosed
Compliance›NIST CSF 2.0›Mappings
MappingsAssessments reused from other standards
Subcategory and related controlStatusStandard
PR.AA-01 · Identity managementReusedISO 27001
RS.MA-01 · Incident responseReusedNIS2
ID.AM-01 · Hardware inventoryReusedISO 27001
GV.SC-01 · Supply chain riskReviewDORA
Assess once
If you already manage ISO 27001, NIS2 or DORA in GlobalSuite®, you reuse those assessments in the related subcategories.
Govern, backed by data
The new GV function draws on the risk module: appetite, owners and reporting to the board.
Supply chain built in
Assess your suppliers in the third-party risk module and feed the results straight into GV.SC.
NIST CSF fits with what you already do
NIST CSF
Current and target profiles, action plan and mappings to other standards.
You are hereISO 27001
The certifiable management system that shares many of its controls.
See solution →NIS2
The EU cybersecurity obligation for essential and important sectors.
See solution →DORA
The EU regulation on digital operational resilience for the financial sector.
See solution →
NIST CSF: frequently asked questions
Is NIST CSF mandatory?
No. It's a voluntary framework and there's no certification. Even so, many organisations adopt it because their parent company, customers or insurers ask for it, or because they want a common language for discussing cybersecurity with senior management.
What changes in version 2.0?
Version 2.0, published in February 2024, widens the scope to any organisation, not just critical infrastructure, and adds the Govern function, which covers strategy, roles, policies and supply chain risk.
What are the Tiers?
They're four levels (Partial, Risk Informed, Repeatable and Adaptive) that describe how rigorously an organisation governs and manages its cybersecurity risk. They aren't a compliance score. They help you see where you stand and decide how far you want to go.
What is a profile?
It's a snapshot of the organisation against the framework's subcategories. The current profile shows where you are; the target profile, where you want to be. The gap between them is your action plan.
How does it relate to ISO 27001?
They share many controls, and NIST itself publishes references that map the framework's subcategories to other standards. If you already run an ISMS, a good part of the work is done.
Does it help me comply with NIS2?
It helps, because many measures overlap, but it's no substitute. NIS2 has its own obligations, such as incident reporting and the accountability of management bodies, which you need to cover separately.
The Cybersecurity Framework is published by the US National Institute of Standards and Technology (NIST).
Your NIST CSF profile,
always up to date.
We’ll show you your current and target profiles in GlobalSuite®.