





SOX controls tested and ready for the auditor
Risk and control matrix, testing and Section 302 and 404 certifications on one platform. No more chasing evidence by email.


What SOX is and what you will be asked for
The Sarbanes-Oxley Act was passed in the United States in 2002 to protect investors after the accounting scandals of that era. It requires companies listed in the US to show that their financial reporting is reliable and that the internal control behind it works. If your group is listed there, your subsidiary is in scope too.
The heaviest lift is Section 404: management assesses internal control over financial reporting every year and, at the largest companies, the external auditor issues its own opinion. That takes documented controls, tests backed by evidence and properly classified deficiencies.
- Law
- Sarbanes-Oxley Act, United States, 2002
- Regulator
- The SEC; the PCAOB oversees auditors
- Applies to
- Companies listed in the US and their subsidiaries, including foreign ones
- Framework
- Usually COSO 2013, Internal Control
- Frequency
- Quarterly certification and annual assessment
1
Scoping
Pick the significant accounts and processes and the risk of misstatement in each.
2
Documentation
Describe the processes and build the risk and control matrix.
3
Testing
Test the design and operating effectiveness of every key control and keep the evidence.
4
Certification
Management signs off and the external auditor reviews the result.
The three sections that matter most
302
Management certification
The CEO and CFO certify the financial statements and the controls over the information disclosed in each periodic report.
404
Internal control assessment
Management assesses internal control over financial reporting every year. At the largest companies, the external auditor gives its opinion.
906
Criminal liability
Signing a certification you know to be false can lead to fines and prison sentences for those who sign it.
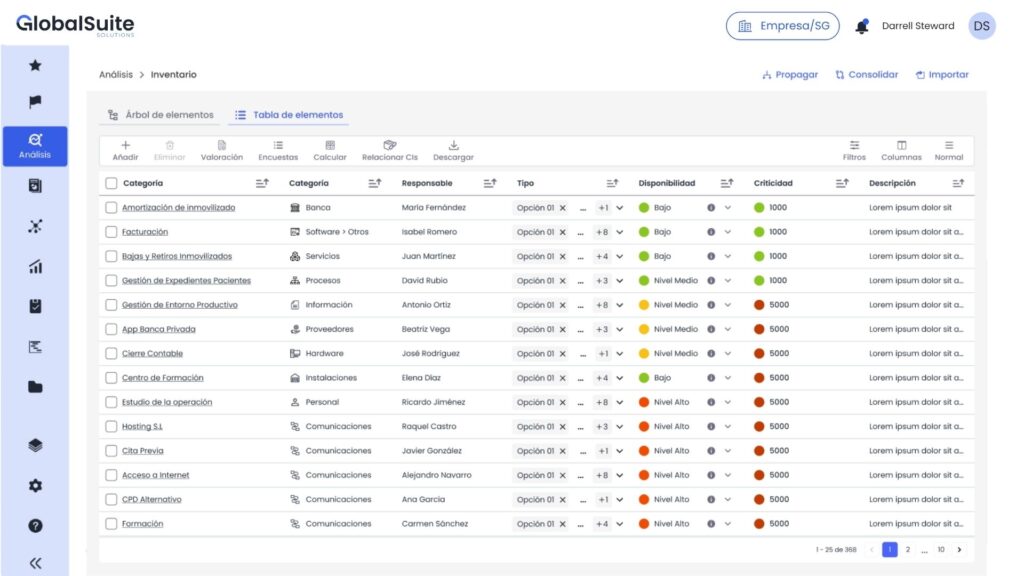
Get SOX-ready in GlobalSuite®
From scoping to certification in one place, with every control linked to its owner, its test and its evidence.
Compliance›SOX›Scoping
Significant processesFY 2026 · 4 processes in scope
CodeProcessAccountRisk
PR-01
Revenue and receivables
Revenue recognition
SalesHighPR-02
Purchasing and payables
Invoices and suppliers
PayablesMediumPR-03
Payroll
Joiners, leavers and payments
Staff costsMediumPR-04
Financial close
Manual entries and adjustments
VariousHighCompliance›SOX›Risk and control matrix
Key controls38 controls · 21 key
ControlOwnerFrequencyType
Bank reconciliation reviewedJRJ. RamosMonthlyManual
Manual journal entry approvalMRM. RuizDailyManual
Credit block on sales ordersALA. LópezContinuousAutomated
ERP access reviewCPC. PérezQuarterlyManual
Compliance›SOX›Effectiveness testing
16
No exceptions
3
With exceptions
2
Pending
TestResultDate
Bank reconciliation · 2-month sampleEffective14 Oct
Manual entries · sample of 251 exception9 Oct
ERP access review · Q3Effective2 Oct
Provisions calculationPending—
Compliance›SOX›Deficiencies
Deficiencies and remediation3 open · fiscal year closes in December
CodeDeficiencyClassificationStatus
DF-01
Entry posted without approval
Manual journal entry control
DeficiencyIn progressDF-02
Generic user in the ERP
Segregation of duties
SignificantOpenDF-03
Late reconciliation
Treasury
DeficiencyClosedOne control, several standards
The same control covers SOX, your local ICFR requirements and your internal audit. Document it and test it once.
Cascading sub-certifications
Each process owner signs off their part before management does. You keep a record of who signed what and when.
The auditor finds it all
Tests, samples and evidence organised by control, so the external auditor does not have to ask for them one by one.
SOX fits with what you already do
SOX
Scoping, control matrix, testing, deficiencies and Section 302 and 404 certifications.
You are hereInternal audit
Plan and run your audits with the same tests and evidence you use for SOX.
See solution →Risk management
Financial reporting risks inside the enterprise-wide risk map.
See solution →Compliance
SOX obligations alongside every other standard the group has to meet.
See solution →
SOX frequently asked questions
Who does SOX apply to?
To companies registered with the SEC because they are listed in the United States, including foreign ones. Subsidiaries of those groups, wherever they are, usually have to document and test their controls so the group can certify.
What exactly does Section 404 require?
Management must assess the effectiveness of internal control over financial reporting (ICFR) every year and report on it in the annual report. At larger companies, the external auditor also issues an opinion on that internal control.
What is the difference between a significant deficiency and a material weakness?
A material weakness exists when there is a reasonable possibility that a material misstatement in the financial statements will not be prevented or detected on time. A significant deficiency is less severe, but important enough to merit the attention of those charged with governance.
Which control framework is used?
Most companies use COSO 2013, the COSO Internal Control Integrated Framework. It is also the reference for many local internal control over financial reporting rules, so much of the work carries over.
Can you manage SOX in spreadsheets?
You can, and many companies start that way. The trouble comes with several subsidiaries, hundreds of controls and an auditor asking for evidence every year. Keeping controls, tests and deficiencies in one place avoids duplicate versions and lost information. There is more background in our article What is the Sarbanes-Oxley Act (SOX)?.
Walk into your SOX audit
with everything tested.
We will show you your control matrix and your tests in GlobalSuite®.