





Your AI risk, managed with the NIST framework
Govern, map, measure and manage every AI system with the NIST AI RMF, then reuse the work for ISO 42001 and the AI Act.


What the NIST AI RMF is and what you will be asked for
The AI Risk Management Framework is the framework from NIST, the US standards body, for managing the risks of artificial intelligence systems. It is voluntary, but it has become a benchmark: customers, partners and public bodies use it to ask how you keep your AI under control.
It is built around four functions, broken down into categories and subcategories. You choose which ones apply to each system and build a profile: where you are today and where you want to be. Since July 2024 it also has a dedicated profile for generative AI.
- Issued by
- NIST, the US National Institute of Standards and Technology
- Version
- AI RMF 1.0, January 2023
- Status
- Voluntary, for any sector and organisation size
- Structure
- Four functions, with categories and subcategories
- Companions
- The Playbook and the generative AI profile (NIST AI 600-1)
1
Inventory
Log your AI systems, what they are for, the data they use and who owns them.
2
Current profile
Assess which subcategories of the framework each system already covers.
3
Target profile
Set where each system needs to be based on its risk, and plan how to close the gaps.
4
Monitoring
Measure, review and update the profile throughout the life of the system.
The four functions of the framework
Govern
Set the ground rules
Policies, roles, culture and accountability. It runs across the other three.
Map
Know the context
What each system is for, who it affects and what could go wrong.
Measure
Test and track
Metrics and testing for reliability, safety, bias and robustness.
Manage
Act on the risk
Prioritise and treat risks, and respond when something fails.
Trustworthy AI is:
Valid and reliable
Safe
Secure and resilient
Accountable and transparent
Explainable and interpretable
Privacy-enhanced
Fair, with harmful bias managed
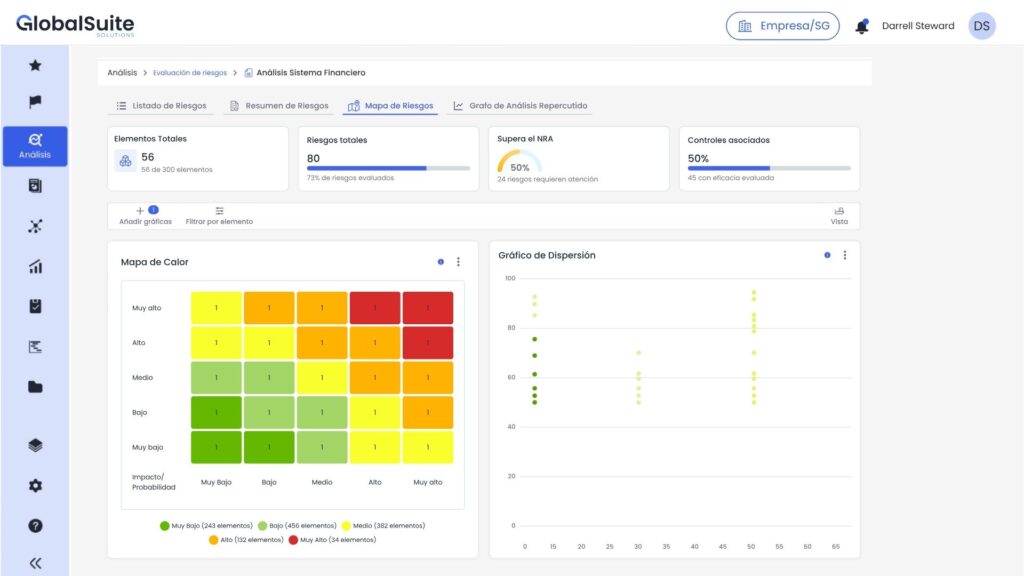
Put the NIST AI RMF to work in GlobalSuite®
From inventory to monitoring in one place, with every subcategory linked to its owner and its evidence.
Compliance›NIST AI RMF›Inventory
AI systems18 systems · 5 third-party
CodeSystemRiskProfile
IA-01
Customer scoring model
In-house · credit decisions
HighReviewedIA-04
Generative assistant for customer service
Third-party · customer replies
MediumIn progressIA-09
Payment fraud detection
In-house · real-time alerts
HighReviewedIA-15
Inbound email classifier
Internal · productivity
LowPendingCompliance›NIST AI RMF›Profile IA-01
41
Covered
17
Partial
9
Pending
Subcat.Expected outcomeCoverage%
GV 1.1Legal requirements for AI identified100
MP 1.1Purpose and context of use documented90
MS 2.7Security and resilience evaluated60
MS 2.11Fairness and bias evaluated40
MG 4.1Post-deployment monitoring55
Compliance›NIST AI RMF›Risks and actions
Risks and actionsIA-01 · 7 risks identified
ActionOwnerDueStatus
Bias test by age groupPMP. Méndez20 OctIn progress
Human review of rejectionsCGC. García6 OctClosed
Explaining the decision to the customerRVR. Vidal3 NovOpen
Model drift alertPMP. Méndez15 NovIn progress
Compliance›NIST AI RMF›Evidence
EvidenceIA-01 · latest profile review
EvidenceStatusReviewed
Model card approvedCurrenttoday
Robustness test reportUp to date4 d
Quarterly bias analysisPending1 wk
AI committee minutesFiled2 wk
One piece of work, three frameworks
What you do for the NIST AI RMF carries over to ISO 42001 and the AI Act obligations, with no duplicate inventories or evidence.
Generative AI, handled on its own
The generative AI risks in the NIST AI 600-1 profile are managed in every system that uses it.
Your suppliers’ AI too
Assess third-party AI systems with questionnaires from the third-party risk module.
The NIST AI RMF fits with what you already do
NIST AI RMF
AI inventory, profile by subcategory, risks, actions and evidence.
You are hereISO 42001
The certifiable AI management system, which shares many of the same controls.
See solution →AI Act
The EU regulation on AI, mandatory if your systems are used in the EU.
See solution →AI Governance
The GlobalSuite® module for governing all your AI systems.
See solution →
Frequently asked questions about the NIST AI RMF
Is the NIST AI RMF mandatory?
No. It is a voluntary framework. Even so, many organisations adopt it because customers or partners ask how they manage AI risk and want a recognised reference.
Does it apply outside the United States?
Yes. It is not tied to any specific law and can be used in any country and sector. In Europe it is often combined with ISO 42001 and the AI Act.
How is it different from ISO 42001?
ISO 42001 is a certifiable management system. The NIST AI RMF is a risk management framework with no certification. They complement each other: many measures work for both.
And from the AI Act?
The AI Act is a binding regulation in the European Union, with obligations that depend on each system’s risk level. The NIST AI RMF requires nothing, but it helps you organise the work the AI Act demands.
What is the generative AI profile?
It is NIST AI 600-1, published in July 2024. It applies the framework to risks specific to generative AI, such as made-up information, harmful content or data leakage.
Where do I start?
With an inventory of your AI systems, including third-party ones. From there you can assess each system’s current profile and decide which subcategories to prioritise.
Your AI,
with the NIST framework.
We will show you your AI RMF profile set up in GlobalSuite®.