Keep your methodology
Your scales, your risk matrix and your own controls sit alongside Annex A. You start with what you already have.
Platform
All-in-one GRC platform
AI built into every module
The common engine behind every module
GRC tailored to your industry
Connect GlobalSuite® to your tools
Standards and frameworks
ISO standards
Regulations
Document once, comply with all.
Resources
 Success storyEMT Madrid centralises its data protection management in GlobalSuite®Read the story

 G2 reviewsWhat the people who use GlobalSuite® every day say about itRead reviewsA customer? Leave a review
Popular searches
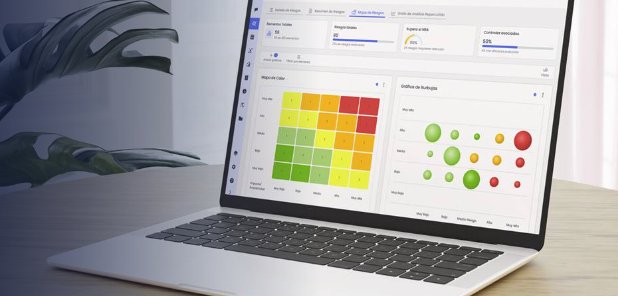
Requirements, risks, controls, evidence and audits in one place, with the year's tasks and reminders running on their own.
4.4 · 105 reviews on G2
2,000+ companies trust GlobalSuite®
What the standard asks for, what you've already done and what's still missing, all on one platform. Screens show sample data.
Every requirement of the standard with its applicability, status and degree of compliance.
Every requirement of the standard with its applicability, status and degree of compliance.
AI reads your documentation and proposes which controls apply to you and why. You review and validate it.
Pick a risk on the asset and the AI suggests the Annex A controls that mitigate it. Add them to the plan and the residual risk is recalculated.
Every piece of evidence in its folder, tagged with the standard, with its version, owner and approval workflow.
The internal audit in the same tool: items, risks reviewed, controls tested and findings.
Every policy and procedure goes through its review and approval workflow before it is published.
Compliance for each part of the standard, in charts ready for the committee.
You set up the workflow once and GlobalSuite® repeats it: it requests, reminds, collects and updates. Your team only steps in when there's a decision to make.
Your scales, your risk matrix and your own controls sit alongside Annex A. You start with what you already have.
Statement of Applicability, risk report and management dashboard, up to date and ready to download.
Before each audit, the agent reviews the Statement of Applicability, finds the controls with no evidence and drafts the plan. You just sign it off.
Your ISMS already covers a large part of what NIS2 and DORA require. In GlobalSuite® each control is mapped to every standard that asks for it, so you don't start from scratch.
Our own estimate of how much of each standard is covered: each requirement counts in full if it is covered the same way and half if only partly. Each standard adds its own requirements.
GlobalSuite® connects to your ecosystem via API. Data comes in on its own and nobody has to copy it by hand.
 Power BI
Monitoring
Vulnerabilities
Data lake
And that module is part of the GRC platform. The assets, risks and suppliers you add for ISO 27001 are the same ones used by continuity, privacy and third-party risk.
If you're asked for NIS2 or DORA tomorrow, you start with all of that already in place.
Your team leads the way. GlobalSuite® automates your management system and, if you need it, our consultants support you at whichever step you choose.

Cybersecurity · Latin America
An information security management system makes it easier to set up and maintain a protection framework for our information and our clients', methodically and consistently.
Andrés Suárez AlarcónCompliance and Business Risk · NEOSECURE by SEK
I like the adaptability of GlobalSuite with my methodologies. It helps my organization improve the ISMS functions.
The results of the risk analysis are mathematical calculations and not random, which makes it a valid tool for presenting before a certification.
From day one, the onboarding process was excellent, allowing us to understand the platform really fast, thanks to their top-notch support team. The UI is clean and intuitive, making it easy to use for everyone.
Shall we look at it with your risks and your methodology?
Request a demo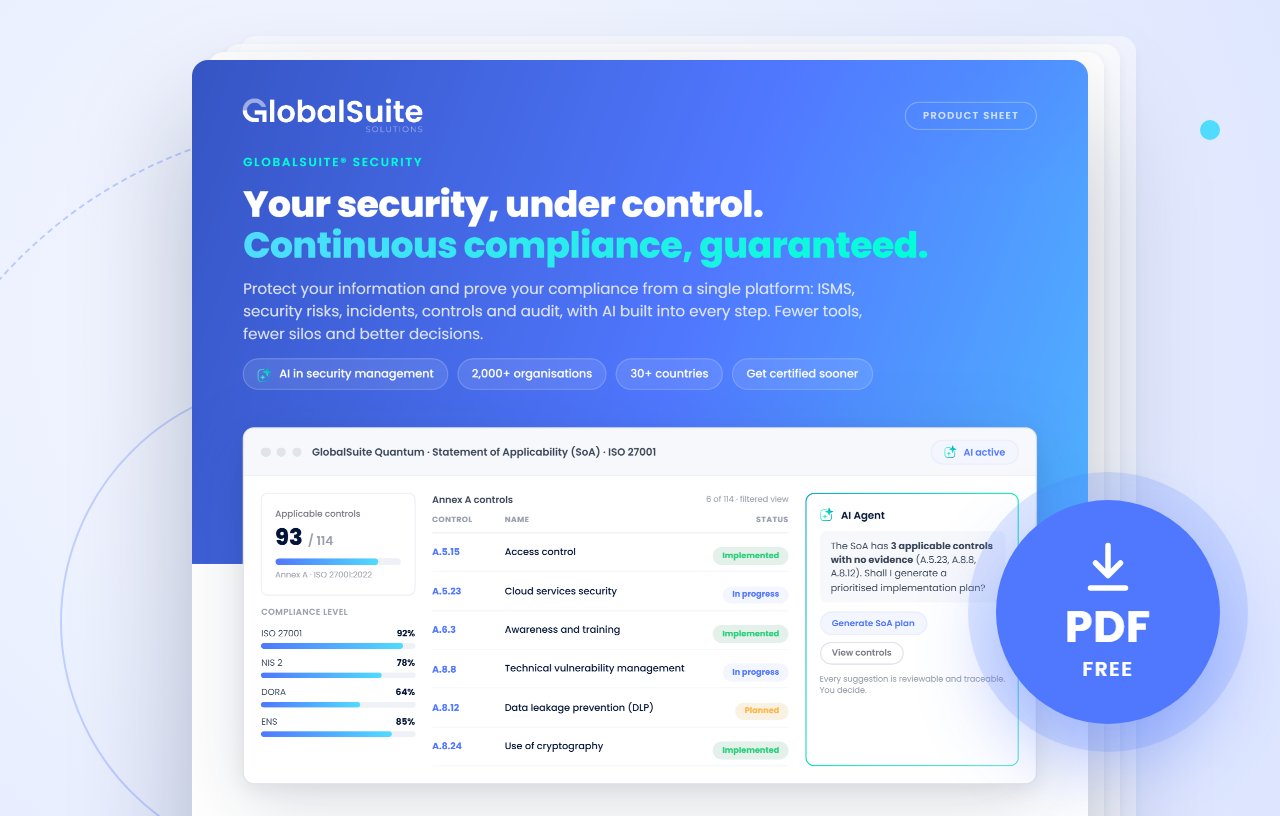 Product sheetGlobalSuite® SecurityYour ISMS assets, controls and evidence in one place, with ISO 27001 preloaded.Download PDF
Compliance, risk, incidents, performance and reporting in the CISO’s day to day.
Download the guide
What DORA is, its key pillars and an action checklist.
Download the guideCan't find your question? Tell us about your case and we'll answer it with your situation in mind.
Tell us about your caseTell us what you need and we’ll show you how GlobalSuite® solves it.