

TPRMThird-Party Risk Management
How a TPRM Software Can Transform Third-Party Risk Management
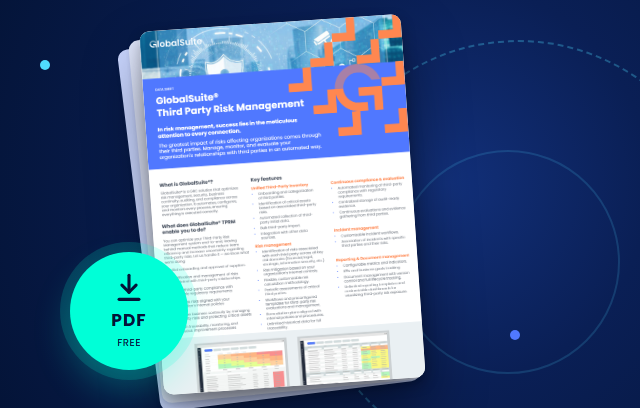
How to identify, assess and mitigate partner and supplier risk with software.
Download the guidePlatform
All-in-one GRC platform
AI built into every module
The common engine behind every module
GRC tailored to your industry
Connect GlobalSuite® to your tools
Standards and frameworks
ISO standards
Regulations
Document once, comply with all.
Resources
 Success storyEMT Madrid centralises its data protection management in GlobalSuite®Read the story

 G2 reviewsWhat the people who use GlobalSuite® every day say about itRead reviewsA customer? Leave a review
Popular searches
Practical guide · 2023
Regulation (EU) 2022/2554What the Digital Operational Resilience Act requires and how to get compliant, in nine pages.
Download the free guideDORA is the EU regulation on digital operational resilience for the financial sector. It sets out how financial entities in the European Union must manage ICT risk, report incidents, test their resilience and oversee their technology providers.
This practical guide sums up what the regulation requires and how to get compliant. It is written for the risk, compliance and security teams who have to put it into practice.
From that date DORA is mandatory for the main players in the European financial sector. It builds on European and international good practice in cyber and operational resilience.
The guide maps DORA to ISO 27001, ISO 27005, ISO 31000, ISO 22301, ISO 22313 and ISO 22317, the GDPR, the Spanish LOPDGDD and the NIS2 Directive. If you already work with any of them, you are a good part of the way there.
How to identify, assess and mitigate partner and supplier risk with software.
Download the guide
The steps to run a BIA and feed its results into your continuity plan.
Download the guide
Seven keys to measure what GRC software delivers.
Download the guide