Keep your methodology
Your scales, your risk matrix and your own controls sit alongside the Article 21 measures. You start with what you already have.
Platform
All-in-one GRC platform
AI built into every module
The common engine behind every module
GRC tailored to your industry
Connect GlobalSuite® to your tools

Standards and frameworks
ISO standards
Regulations
Document once, comply with all.
Resources
 Success storyEMT Madrid centralises its data protection management in GlobalSuite®Read the story

 G2 reviewsWhat the people who use GlobalSuite® every day say about itRead reviewsA customer? Leave a review
Popular searches
The Article 21 measures, risks, suppliers and incidents with their 24-hour, 72-hour and one-month deadlines, all in one place and with management kept informed.
4.4 · 105 reviews on G2
2,000+ companies trust GlobalSuite®
What the Directive asks for, what you've already done and what's still missing, all on one platform. Screens show sample data.
Every obligation in the directive with its applicability, status and degree of compliance.
Every obligation in the directive with its applicability, status and degree of compliance.
The group companies in the organisational structure, each with its NIS2 entity type and its owner.
All hazards on one map: cyberattacks, supplier failures and utility outages, from inherent to residual risk.
The AI reviews contracts and accesses, finds suppliers that get into your systems but are missing from the register, and leaves them ready to assess.
Every incident with its priority, the service and supplier affected, and an alert when it has to be reported.
Policies and the treatment plan go through approval by the management body, with date and signature, as Article 20 requires.
Compliance with each Article 21 measure, in charts ready for the board.
You set up the workflow once and GlobalSuite® repeats it: it requests, reminds, collects and updates. Your team only steps in when there's a decision to make.
Your scales, your risk matrix and your own controls sit alongside the Article 21 measures. You start with what you already have.
Measure status, board report and incident log, up to date and ready to download.
Before each review, the agent goes through the Article 21 measures, finds the ones with no evidence and drafts the plan. You just sign it off.
The NIS2 measures already cover a large part of what ISO 27001 and DORA require. In GlobalSuite® each control is mapped to every standard that asks for it, so you don't start from scratch.
Our own estimate of how much of each standard is covered: each requirement counts in full if it is covered the same way and half if only partly. Each standard adds its own requirements.
GlobalSuite® connects to your ecosystem via API. Data comes in on its own and nobody has to copy it by hand.
 Power BI
Monitoring
Vulnerabilities
Data lake
And that module is part of the GRC platform. The assets, risks and suppliers you add for NIS2 are the same ones used by continuity, privacy and third-party risk.
If you're also asked for ISO 27001 or DORA, you start with all of that already in place.
Your team leads the way. GlobalSuite® automates your management system and, if you need it, our consultants support you at whichever step you choose.
Cybersecurity · Latin America
An information security management system makes it easier to set up and maintain a protection framework for our information and our clients', methodically and consistently.
Andrés Suárez AlarcónCompliance and Business Risk · NEOSECURE by SEK
I like the adaptability of GlobalSuite with my methodologies. It helps my organization improve the ISMS functions.
The results of the risk analysis are mathematical calculations and not random, which makes it a valid tool for presenting before a certification.
From day one, the onboarding process was excellent, allowing us to understand the platform really fast, thanks to their top-notch support team. The UI is clean and intuitive, making it easy to use for everyone.
Shall we look at it with your risks and your methodology?
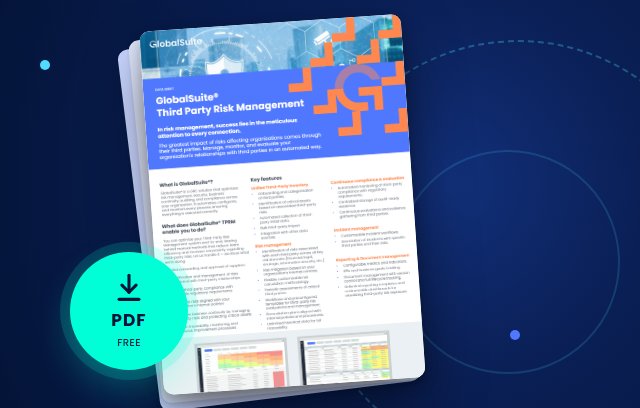
Request a demo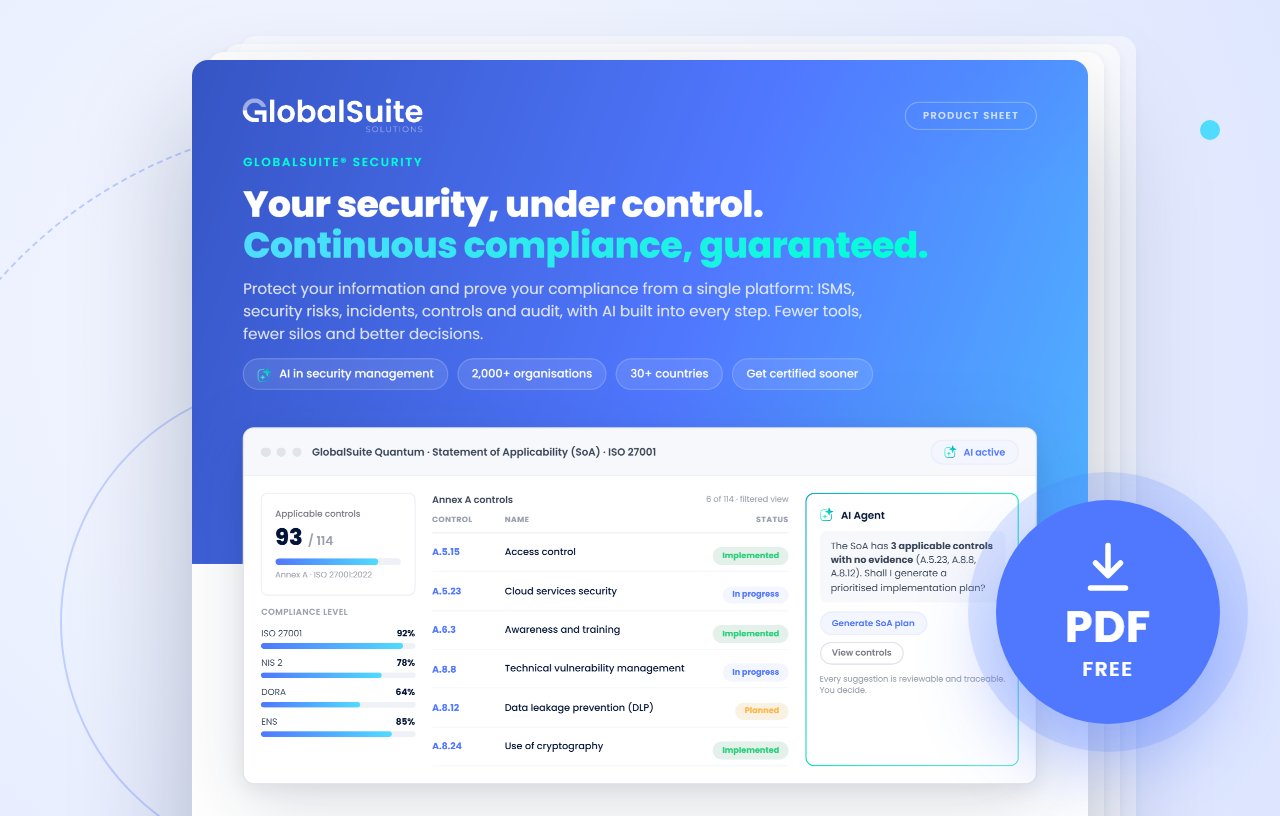 Product sheetGlobalSuite® SecurityYour ISMS assets, controls and evidence in one place, with ISO 27001 preloaded.Download PDF
Compliance, risk, incidents, performance and reporting in the CISO’s day to day.
Download the guide
What DORA is, its key pillars and an action checklist.
Download the guideCan't find your question? Tell us about your case and we'll answer it with your situation in mind.
Tell us about your caseTell us what you need and we’ll show you how GlobalSuite® solves it.