





TISAX® without spreadsheets or surprises at assessment time
Prepare your VDA ISA self-assessment, close the gaps and share your labels with your automotive customers.


What TISAX is and what you’ll be asked for
TISAX is how the automotive industry checks the information security of its suppliers. German carmakers created it through the VDA, and it is run by the ENX Association. If you work with an OEM or a tier 1 supplier and handle their drawings, data or prototypes, expect it to be a condition for signing or renewing a contract.
It isn’t a certification. An accredited audit provider assesses you against the VDA ISA catalogue, and the result is a set of labels you share with your customers through the ENX portal. One assessment covers all of them, so you don’t need a separate audit for every carmaker.
- Run by
- ENX Association, on behalf of the VDA
- Catalogue
- VDA ISA version 6, based on ISO/IEC 27001
- Applies to
- Suppliers and service providers in the automotive sector
- Outcome
- Labels per scope, visible to the customers you choose
- Validity
- 3 years
1
ENX registration
You register the company, define the scope and pick the labels your customers require.
2
Self-assessment
You work through the VDA ISA catalogue control by control. The general target is maturity level 3.
3
Assessment
An accredited audit provider reviews your evidence, remotely or on site.
4
Labels
Once the measures are closed, ENX publishes the result and you share it with your customers.
The three assessment levels
AL1
Self-assessment
You complete it yourself and nobody checks it. Very few customers accept it for sharing results.
AL2
Plausibility check
The auditor reviews your self-assessment and evidence and interviews you by video call.
For information with a high protection need.
AL3
Comprehensive verification
A full review with an on-site visit, interviews and inspection of your controls.
For very high protection needs and prototypes.
Most requested labels:
Confidential information
Strictly confidential
High availability
Prototype parts
Test vehicles
Data protection
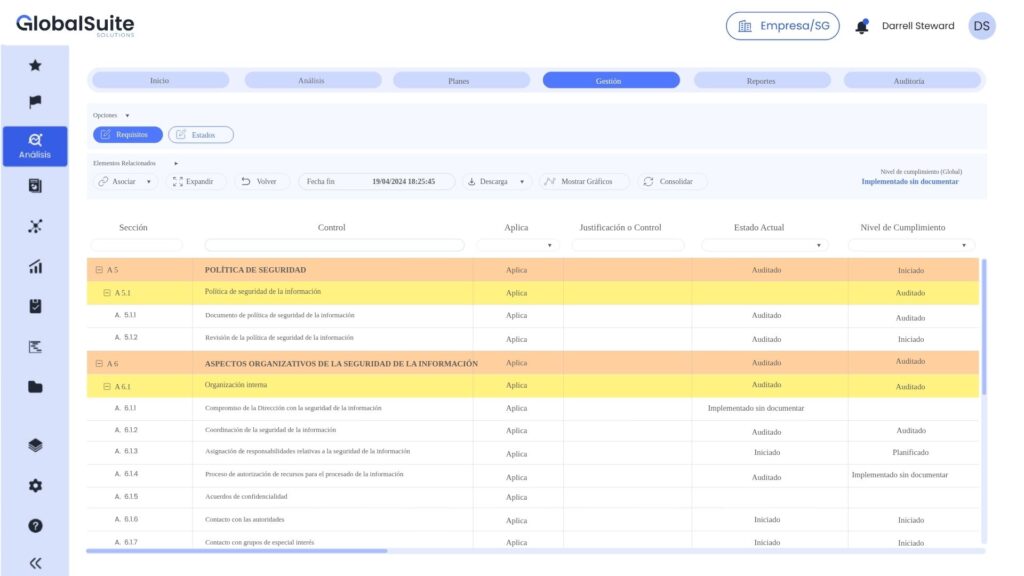
Get ready for TISAX in GlobalSuite®
From scope to labels in one place, with every control linked to its owner and its evidence.
Compliance›TISAX›Scope
Assessment scope2 locations · 4 labels requested
CodeScopeLabelLevel
AL-01
Valladolid engineering office
Component design for OEMs
ConfidentialAL2AL-02
Valladolid engineering office
Drawings for a new platform
Strictly conf.AL3AL-03
Martorell plant
Pre-series parts assembly
Prototype partsAL3AL-04
Martorell plant
Customer employee data
DataAL2Compliance›TISAX›VDA ISA self-assessment
29
On target
9
Below target
3
No evidence
ControlRequirementMaturity / target 3Level
1.1.1Information security policies3
1.3.1Identification of information assets2
1.4.1Information security risk management3
1.6.1Reporting of security events2
1.2.4External IT service providers1
Compliance›TISAX›Action plan
Action plan12 actions · 7 closed
ActionOwnerDueStatus
Asset inventory by locationJRJ. Ramos15 NovIn progress
TISAX clauses in supplier contractsMLM. López30 NovOpen
Procedure for notifying the customer of incidentsLGL. Gil8 NovClosed
Access control for the prototype areaAPA. Pérez22 NovIn progress
Compliance›TISAX›Evidence
Evidence and renewalLabels valid until March 2029
EvidenceStatusReviewed
Security policy signed by managementCurrenttoday
Visitor log for the prototype areaUp to date3 d
Awareness training 2026Pending1 wk
Audit provider reportFiled2 wk
Build on your ISMS
VDA ISA is based on ISO/IEC 27001. If you already manage it in GlobalSuite®, many of the controls are covered and you only work on the differences.
Prototype protection
Dedicated controls for parts, test vehicles, events and shoots, with their evidence kept apart from everything else.
Your suppliers count too
Send questionnaires to your subcontractors and track their TISAX labels from the third-party risk module.
TISAX fits with what you already do
TISAX
VDA ISA assessment, action plan, evidence and label renewal.
You are hereISO 27001
The security management system VDA ISA is built on.
View solution →NIS2
Motor vehicle manufacturing falls within its scope. Many controls overlap.
View solution →GDPR
The TISAX data protection labels check your compliance as a processor.
View solution →
TISAX frequently asked questions
Is TISAX a certification?
No. It’s an information security assessment. The result is a set of labels that ENX publishes on its portal, and you decide which customers can see them. Your customers check them there, so you don’t have to send them reports.
Who needs TISAX?
Suppliers and service providers that handle sensitive information from carmakers or their suppliers: engineering firms, parts manufacturers, logistics companies, agencies, software developers and IT companies. It’s usually required in the contract or when you’re approved as a supplier.
Which assessment level will I need?
Your customer sets it based on the information you’ll handle. A high protection need calls for AL2, with an evidence review and a remote interview. Very high protection and prototypes call for AL3, with a visit to your premises.
How long are the labels valid?
Three years. After that, you need to repeat the assessment. It pays to keep your evidence up to date throughout the period so that renewal doesn’t start from scratch.
How does it relate to ISO 27001?
The VDA ISA catalogue is based on ISO/IEC 27001 and adds sector-specific requirements, such as prototype protection. Having ISO 27001 helps a lot, but it doesn’t replace TISAX: the assessment is different, and your automotive customers will still ask for the labels.
How long does it take to prepare?
It depends on where you’re starting from and which labels you need. With an ISMS already in place, the work focuses on the VDA ISA differences and the prototype measures. You’ll find more detail in our TISAX compliance guide.
TISAX® is a registered trademark of ENX Association. GlobalSuite Solutions is not a TISAX audit provider.