
GRC FAQFrequently asked questions
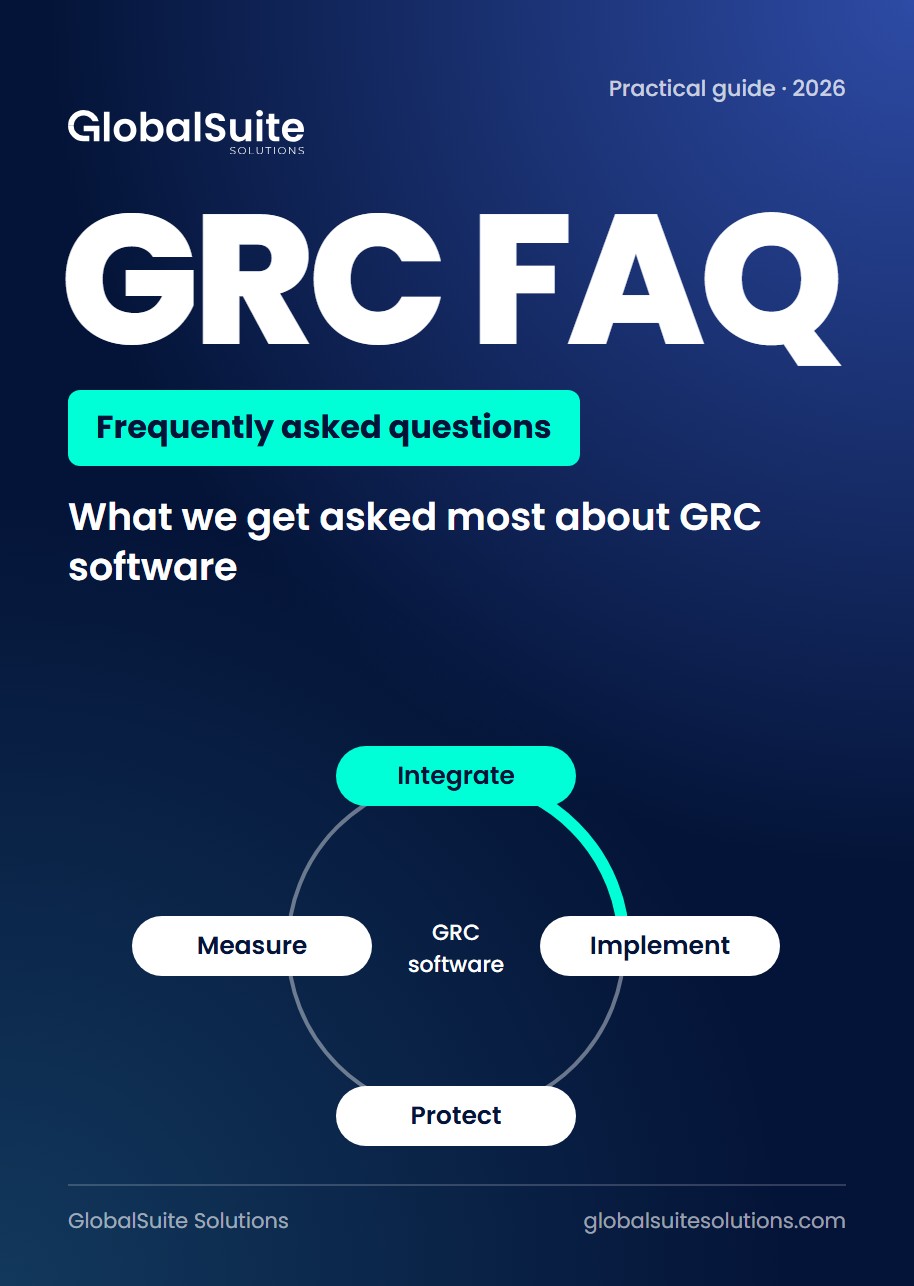
What we get asked most about GRC software
Plain answers on integrations, implementation, return, risk and data security in GlobalSuite®.
Download the guidePlatform
All-in-one GRC platform
AI built into every module
The common engine behind every module
GRC tailored to your industry
Connect GlobalSuite® to your tools

Standards and frameworks
ISO standards
Regulations
Document once, comply with all.
Resources
 Success storyEMT Madrid centralises its data protection management in GlobalSuite®Read the story

 G2 reviewsWhat the people who use GlobalSuite® every day say about itRead reviewsA customer? Leave a review
Popular searches
Practical guide · 2026
Regulation (EU) 2016/679How to run GDPR and LOPDGDD compliance as a management system and be able to prove it at any time.
Download the free guideThe General Data Protection Regulation (GDPR) and Spain's LOPDGDD turn data protection into a management system, with obligations for controllers and processors. The idea behind it is accountability: complying is not enough, you have to be able to prove it.
This guide goes through each element the regulation introduces and how it is managed in GlobalSuite®. It is for Data Protection Officers and privacy leads who need structure and want to stop depending on spreadsheets.
Serious infringements can cost up to 10 million euros or 2% of worldwide annual turnover, and very serious ones up to 20 million euros or 4%, whichever is higher. Breaches that could harm data subjects must be notified to the supervisory authority within 72 hours.
Because GlobalSuite® is an integrated platform, you can grow from data protection into ISO 27001 or Spain's National Security Framework (ENS) and reuse the work already done.
Plain answers on integrations, implementation, return, risk and data security in GlobalSuite®.
Download the guide
Every requirement of a compliance management system, from scope to audit, run in GlobalSuite®.
Download the guide
Deadlines, roles, risk categories, fines and first steps to prepare for the AI Act.
Download the guide