

GRC blog by GlobalSuite Solutions
Regulation, risk, cybersecurity and product news, explained by the experts who build GlobalSuite® every day.
What's new in GlobalSuite® Quantum
Every release, explained: what changes in the platform and how your team benefits.
Product
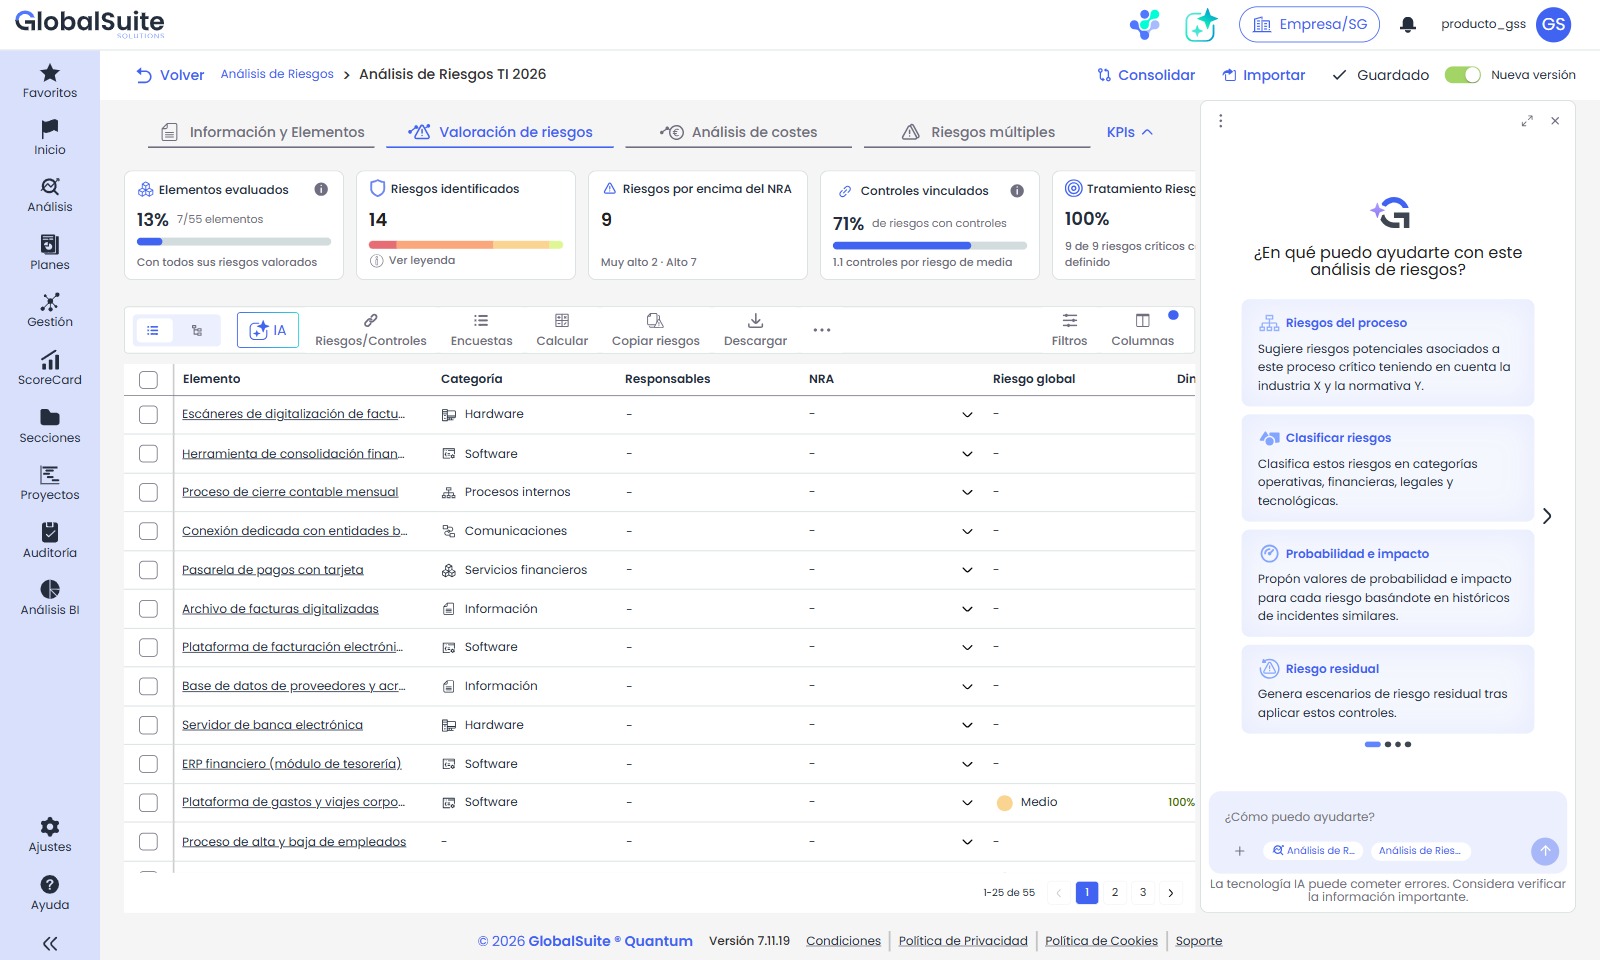
5 minGlobalSuite® Quantum v7.12: GlobalSuite® MCP, the AI Agent for Risk, and a redesigned Risk Analysis and Assessment
Learn more
Product
7 minGlobalSuite® Quantum: Integration with SharePoint, OneDrive, and Google Drive
Learn more AI-powered
Product
3 minRisk Quantification in GlobalSuite Quantum: simulate, quantify and decide
Learn moreBrowse all articles
Topics
CybersecuritySecurity
4 minInformation security vs cybersecurity: what is the difference?
Learn more
Security
6 minTISAX labels: which one you need and which assessment level (AL2 or AL3)
Learn more
Security
3 minConnection between ISO 27005 and ISO 27001: Boost your Information Security Risk Management
Learn more
Security
2 minWeb “Cookies” Turn 30 Years Old: Anniversary and Farewell
Learn more
Security
6 minTISAX compliance: what it is and how to prepare
Learn more
Security
4 minDifferences between ISO 27701 and ISO 27018
Learn more
Security
4 minISO 27001: what are the main controls in the standard?
Learn more
Security
6 minWhat is the ISO 27001 standard and what is its purpose?
Learn more
CybersecuritySecurity
4 minDORA Cybersecurity Regulation
Learn more
Security
4 minNew Version ISO 27001:2022
Learn more
Security
6 minThe Main Changes in the ISO 27002:2022 Standard Update
Learn more
Security
5 minThe PDCA cycle in ISO 27001
Learn more
Security
3 minHow to Conduct an Internal Audit of an ISMS Based on ISO 27001
Learn more
Security
4 minISO 27036 – Information Security for Supplier Relationships
Learn more
AuditSecurity
3 minSecurity Audits
Learn more
Security
4 minWhat is the Statement of Applicability (SoA) and what is it for?
Learn more
Security
3 minISO 27018. Security and Protection of Personal Information in the Cloud
Learn more
Security
4 min5 Key steps for implementation of your ISMS
Learn moreShowing 18 of 19 articles