
GRC FAQFrequently asked questions
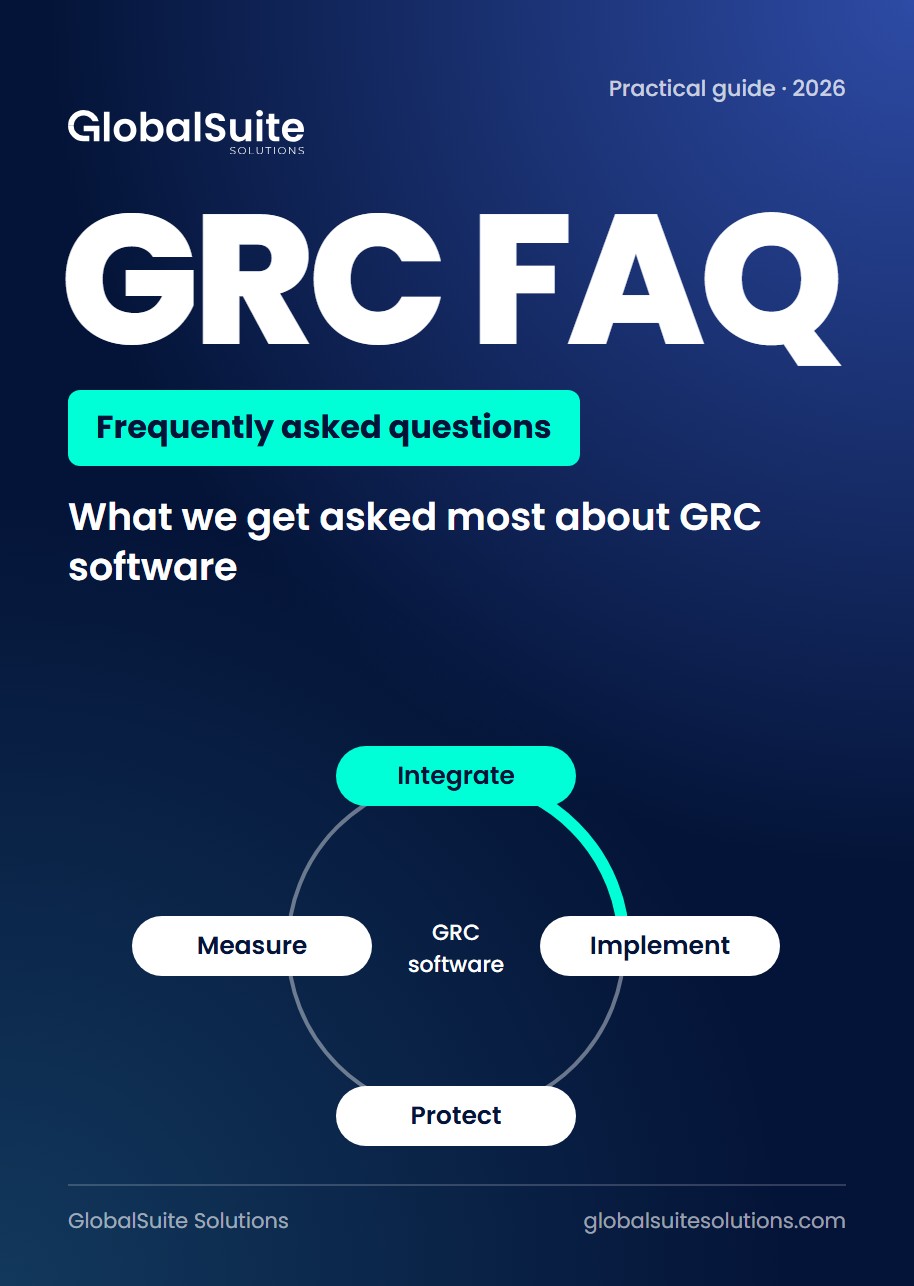
What we get asked most about GRC software
Plain answers on integrations, implementation, return, risk and data security in GlobalSuite®.
Download the guidePlatform
All-in-one GRC platform
AI built into every module
The common engine behind every module
GRC tailored to your industry
Connect GlobalSuite® to your tools

Standards and frameworks
ISO standards
Regulations
Document once, comply with all.
Resources
 Success storyEMT Madrid centralises its data protection management in GlobalSuite®Read the story

 G2 reviewsWhat the people who use GlobalSuite® every day say about itRead reviewsA customer? Leave a review
Popular searches
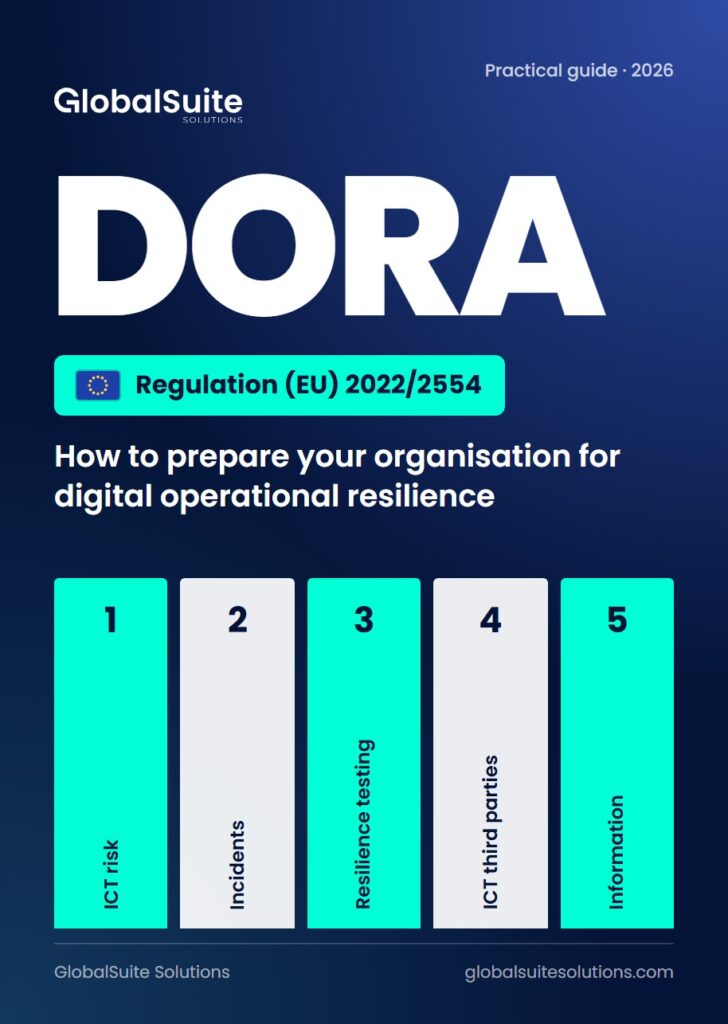
Practical guide · 2026
Regulation (EU) 2022/2554What the Digital Operational Resilience Act requires of financial entities and where to start putting it in place.
Download the free guideDORA is the EU regulation on digital operational resilience for the financial sector. It requires financial entities to show that their digital operations can withstand attacks, failures and supplier outages.
This guide sums up what DORA asks for, what your organisation has to put in place and where to start. It is written for the risk, compliance and security teams who have to put it into practice.
DORA has been mandatory for financial entities in the European Union since that date. It builds on European and international good practice in cyber and operational resilience.
The guide maps DORA to ISO 27001, ISO 27005, ISO 31000, ISO 22301, ISO 22313 and ISO 22317, the GDPR, the Spanish LOPDGDD and the NIS2 Directive. If you already work with any of them, you are a good part of the way there.
Plain answers on integrations, implementation, return, risk and data security in GlobalSuite®.
Download the guide
Every requirement of a compliance management system, from scope to audit, run in GlobalSuite®.
Download the guide
Deadlines, roles, risk categories, fines and first steps to prepare for the AI Act.
Download the guide